Blog
Streamlining Microsoft Entra Implementation with Third-Party Identity Management Support
Microsoft Entra offers a unified Identity and Access Management (IAM) solution that allows organizations to manage users, resources, and permissions in both cloud and on-premises environments. With its features growing more sophisticated, so does the need for an implementation plan—one that considers both internal and external forms of identities.
While most organizations roll out Entra to support initiatives like Zero Trust or identity governance, actually maximizing the potential of the platform requires more than simply flipping a switch. Misconfigurations or planning gaps can lead to security blind spots, user friction, and slowed project progress.
That’s where implementation partners come in. Our consulting services helps organizations implement Microsoft Entra with a focus on long-term scalability, secure access, and clear identity lifecycle management. We also focus particularly on third-party and non-employee identities—an area that's usually overlooked but highly important for organizations involved in vendor, contractors, or partner relationships.
Why the shift to Microsoft Entra may be necessary
As part of this broader shift toward modern identity governance, Microsoft has also officially announced the support end date for Microsoft Identity Manager (MIM), its legacy identity product. Mainstream support will be discontinued in January 2026, with extended support concluding in January 2029. This change represents a tipping point: organizations that continue to use MIM will be required to move over to Microsoft Entra ID or seek other solutions to ensure security, support, and compliance.
For current MIM customers, this isn’t just an upgrade option—it's an opportunity to reassess how their handling identities within the organization, particularly for third-party and non-employee users. Microsoft Entra is a more cloud-directed, scalable, and policy-driven solution, but it does require planning to move away from MIM. Our team assists organizations in making the move confidently and avoiding the common pitfalls of migrating from on-premises identity models to cloud-native ones.
Why Microsoft Entra is powerful — but complex
One identity and access platform
Microsoft Entra brings together a suite of identity, access, and permission management products for cloud and hybrid environments. With Entra ID (formerly Azure AD), Permissions Management, Verified ID, and ID Governance, the platform gives organizations the foundation they need to enable Zero Trust principles, streamline compliance, and protect workforce and non-workforce identities.
Flexible tools with extensive coverage
The platform is built to be adaptable. It has native support for federated identities, role-based access controls, and integrations with HR systems, SaaS applications, and infrastructure providers. For companies looking to unify identity and access management in one model, Entra is a compelling offer.
Implementation is rarely straightforward
That flexibility, however, typically comes with tradeoffs. Each module within Entra has its own settings, dependencies, and integration pathways. Certain features—like automated access reviews or Just-In-Time permissions—require planning in advance to ensure they align with internal processes. Others, like Verified ID, may require coordination between departments that don't typically interact with IAM tools.
Third-party access adds complexity
For companies that have vendors, suppliers, contractors, or other third parties, identity complexities grow. Microsoft Entra ID was developed primarily with the employee lifecycle in mind, so third-party identities are difficult to manage without additional customization. Non-employee users typically don't align with the standard onboarding and offboarding process. They may be from different organizations that have their own identity providers, use different naming conventions, or require project-based access that doesn’t translate directly to typical enterprise roles.
These realities create administrative overhead and increase the risk of misconfigurations, overprovisioning, and visibility gaps. Entra can enable secure third-party access, but only when accomplished as part of a strategy that considers the unique requirements of non-employees and external identity ecosystems.
Common Entra deployment challenges
Implementing Microsoft Entra is rarely a matter of just plug and play. Organizations typically face a mixture of technical, organizational, and process-based blockers—especially with third-party access. Here are some of the most common obstacles that teams face:
Disconnected identity sources
Most organizations deal with identity information in multiple systems—HR systems, contractor databases, vendor portals, even spreadsheets. These disparate sources hinder the creation of a cohesive identity model in Entra. The outcome is duplicate accounts, inconsistent attributes, and poor visibility into who has access to what.
Unclear roles and overprovisioned access
Without a defined role or group template, it's easy to provide more than the necessary access. This is especially prevalent with non-employee users, who are likely to be given permissions based on urgency instead of policy. Over time, this produces permission sprawl and makes enforcing least privilege access more difficult.
Third-party lifecycle gaps
Unlike permanent employees, third-party users might not have formal onboarding and offboarding procedures. Access is occasionally granted ad hoc or by ad-hoc request with little documentation and follow-up. As a result, accounts are active for longer than intended—or in the worst case, are completely unmanaged.
Underused governance features
Entra offers robust governance capabilities, but they need to be purposefully configured. Access reviews, segregation of duties, and approval workflows aren't enforced by default. When they aren't configured, third-party identities can avoid important oversight steps, which elevates the threat of access abuse.
Misconfigured Conditional Access policies
Conditional Access can block dangerous logins or impose MFA requirements, but it must be calibrated very finely. Inconsistent enforcement does the opposite of what is desired—either blocking legitimate access or failing to identify suspicious behavior—specifically for users outside the core workforce.
Limited bandwidth for identity projects
Internal teams are stretched thin in many instances. Without dedicated time or resources, Entra projects grind to a halt. The consequence: opportunities to automate processes, enforce policies, or close long-existing third-party identity management gaps are lost.
Where our services fit in
Microsoft Entra includes robust identity security capabilities, but its full value depends on its proper implementation. Technical capability is not enough—organizations need a strategy that supports their internal processes, governance requirements, and range of identities. That means managing external users like contractors, suppliers, service providers, and other non-employees who often stay outside traditional identity procedures.
Our consulting and implementation services are designed to assist your team at every phase of the process—starting with initial planning all the way through to ongoing governance.
Strategy and readiness planning
The first step is understanding your environment. We help you review your current identity posture and determine what success looks like for your Entra deployment. This includes an in-depth look at how internal and external users are onboarded, how access is added and revoked, and where there are manual processes or risk exposures now.
Key deliverables are:
• A full identity inventory across internal systems, legacy directories, and third-party platforms.
• Employee, contractor, vendor, and partner role and access mapping.
• Identification of unmanaged or inactive accounts across business units.
• Gap analysis of current practices versus Entra capabilities.
• A tailored rollout plan with work phases, schedules, and governance milestones.
This part of the implementation sets the foundation for a deployment that not only provides functionality, but also compliance and sustainability.
Deployment and technical integration
With a clear strategy in place, we can begin the deployment and setup process. We embed Entra's capabilities into your existing systems and processes to remove friction, improve adoption, and provide scalable access management.
Our implementation services include:
• Entra ID setup in hybrid or cloud-native identity environments.
• Department, job function, geography, or access scope-based group and role organization.
• Integration with HRIS platforms, ITSM systems, and procurement software to enable both third-party and employee onboarding.
• Configuration of Verified ID for secure identity verification during vendor or contractor onboarding.
• Creation of bespoke access models to enable Just-In-Time access, temporary credentials, or time-limited entitlements.
We ensure external identities are no longer an afterthought. Our solution introduces order to non-employee identity management—putting them under governance with defined rules, traceability, and timely deactivation.
Governance, automation, and lifecycle management
Many Entra deployments stall after initial configuration since follow-through on governance does not happen. We avoid that by including governance in the solution from the beginning.
Our optimization and governance work includes:
• Scheduling automated access review cycles with employees and non-employees.
• Setting up attestation workflows so that access is reviewed by the right stakeholders (e.g., business managers, vendor owners).
• Tuning Conditional Access policies on user risk score, location, device health, and access sensitivity.
• Enforcing entitlement cleanup to remove unused or redundant access permissions, especially third-party identities.
• Configuration of automatic account deactivation based on project closure, contract expiry dates, or inactivity triggers.
• Creating recurring monitoring processes, reporting dashboards for tracking access patterns, anomalies, and policy drift.
We also help you decide who owns identity governance for different user types—an all-too-familiar issue in federated/big organizations.
Regular support and tuning
Entra is not a one-time deployment. As your organization grows, merges systems, or introduces new business processes, your identity structure must adapt. We offer regular support to help you tune your strategy, deal with new needs, and keep third-party access in line.
Our teams can help with:
• Periodic review and re-orientation of access policies.
• Integrations with new systems or rollouts of Entra modules.
• Embedding Verified ID or Permissions Management in new scenarios.
• Support for internal audits or compliance scans.
Regardless of whether you're starting from scratch or optimizing an existing deployment, we provide the practical know-how and cross-functional insight needed to make Microsoft Entra operational—inside and out, for all who need access.
Use cases we can help enable
Every organization has its own mix of internal and external users, as well as its own set identity management challenges. The following are a few scenarios that reflect the types of projects we help with Microsoft Entra.
Global retail operations
A multiregional retailer needs to streamline identity management for thousands of vendor reps who accessed inventory systems at regional stores. We can help establish Entra Verified ID and Conditional Access policies that automate identity proofing and grant scoped, time-limited access based on project or contract status.
Healthcare provider network
A medical group with operations across several facilities has no centralized process to onboard temporary personnel and specialty contractors. We can deploy automated onboarding and access review workflows with Entra ID Governance, reducing dormant accounts and improving HIPAA compliance.
Energy and infrastructure company
A large energy company struggles with third-party access to operational technology environments. We can implement Entra Permissions Management to gain more visibility into privileged access across systems and implement least privilege policies—without disrupting critical workflows.
All these examples have one thing in common: organizations need identity systems that are flexible, but also the governance and processes to support them.
Why work with Anomalix
Deploying Microsoft Entra is more than just turning on features, it's about building an identity model that suits your business’ needs. That means mapping Entra’s capabilities to how your people, systems, and external users actually operate. It means defining clear ownership, automating access decisions, and having the platform evolve around your business.
We specialize in helping companies do just that. Our team understands the real-world challenges that come with managing identities across departments, regions, and partner ecosystems. Whether you’re introducing governance for the first time or working to bring structure to non-employee access, we offer more than implementation—we offer a path forward.
We take a practical, collaborative approach. You’ll get the benefit of repeatable frameworks, technical depth, and experience working with Entra in complex environments. Just as important, we focus on long-term maintainability—so your team isn’t overwhelmed trying to manage access by hand a year from now.
If you’re dealing with unmanaged identities, limited visibility, or inconsistent third-party access processes, we can help.
Want to get more from your Microsoft Entra deployment? Reach out to our team at info@anomalix.com to schedule a discovery session or Entra readiness assessment.
Written by
More articles
View all articles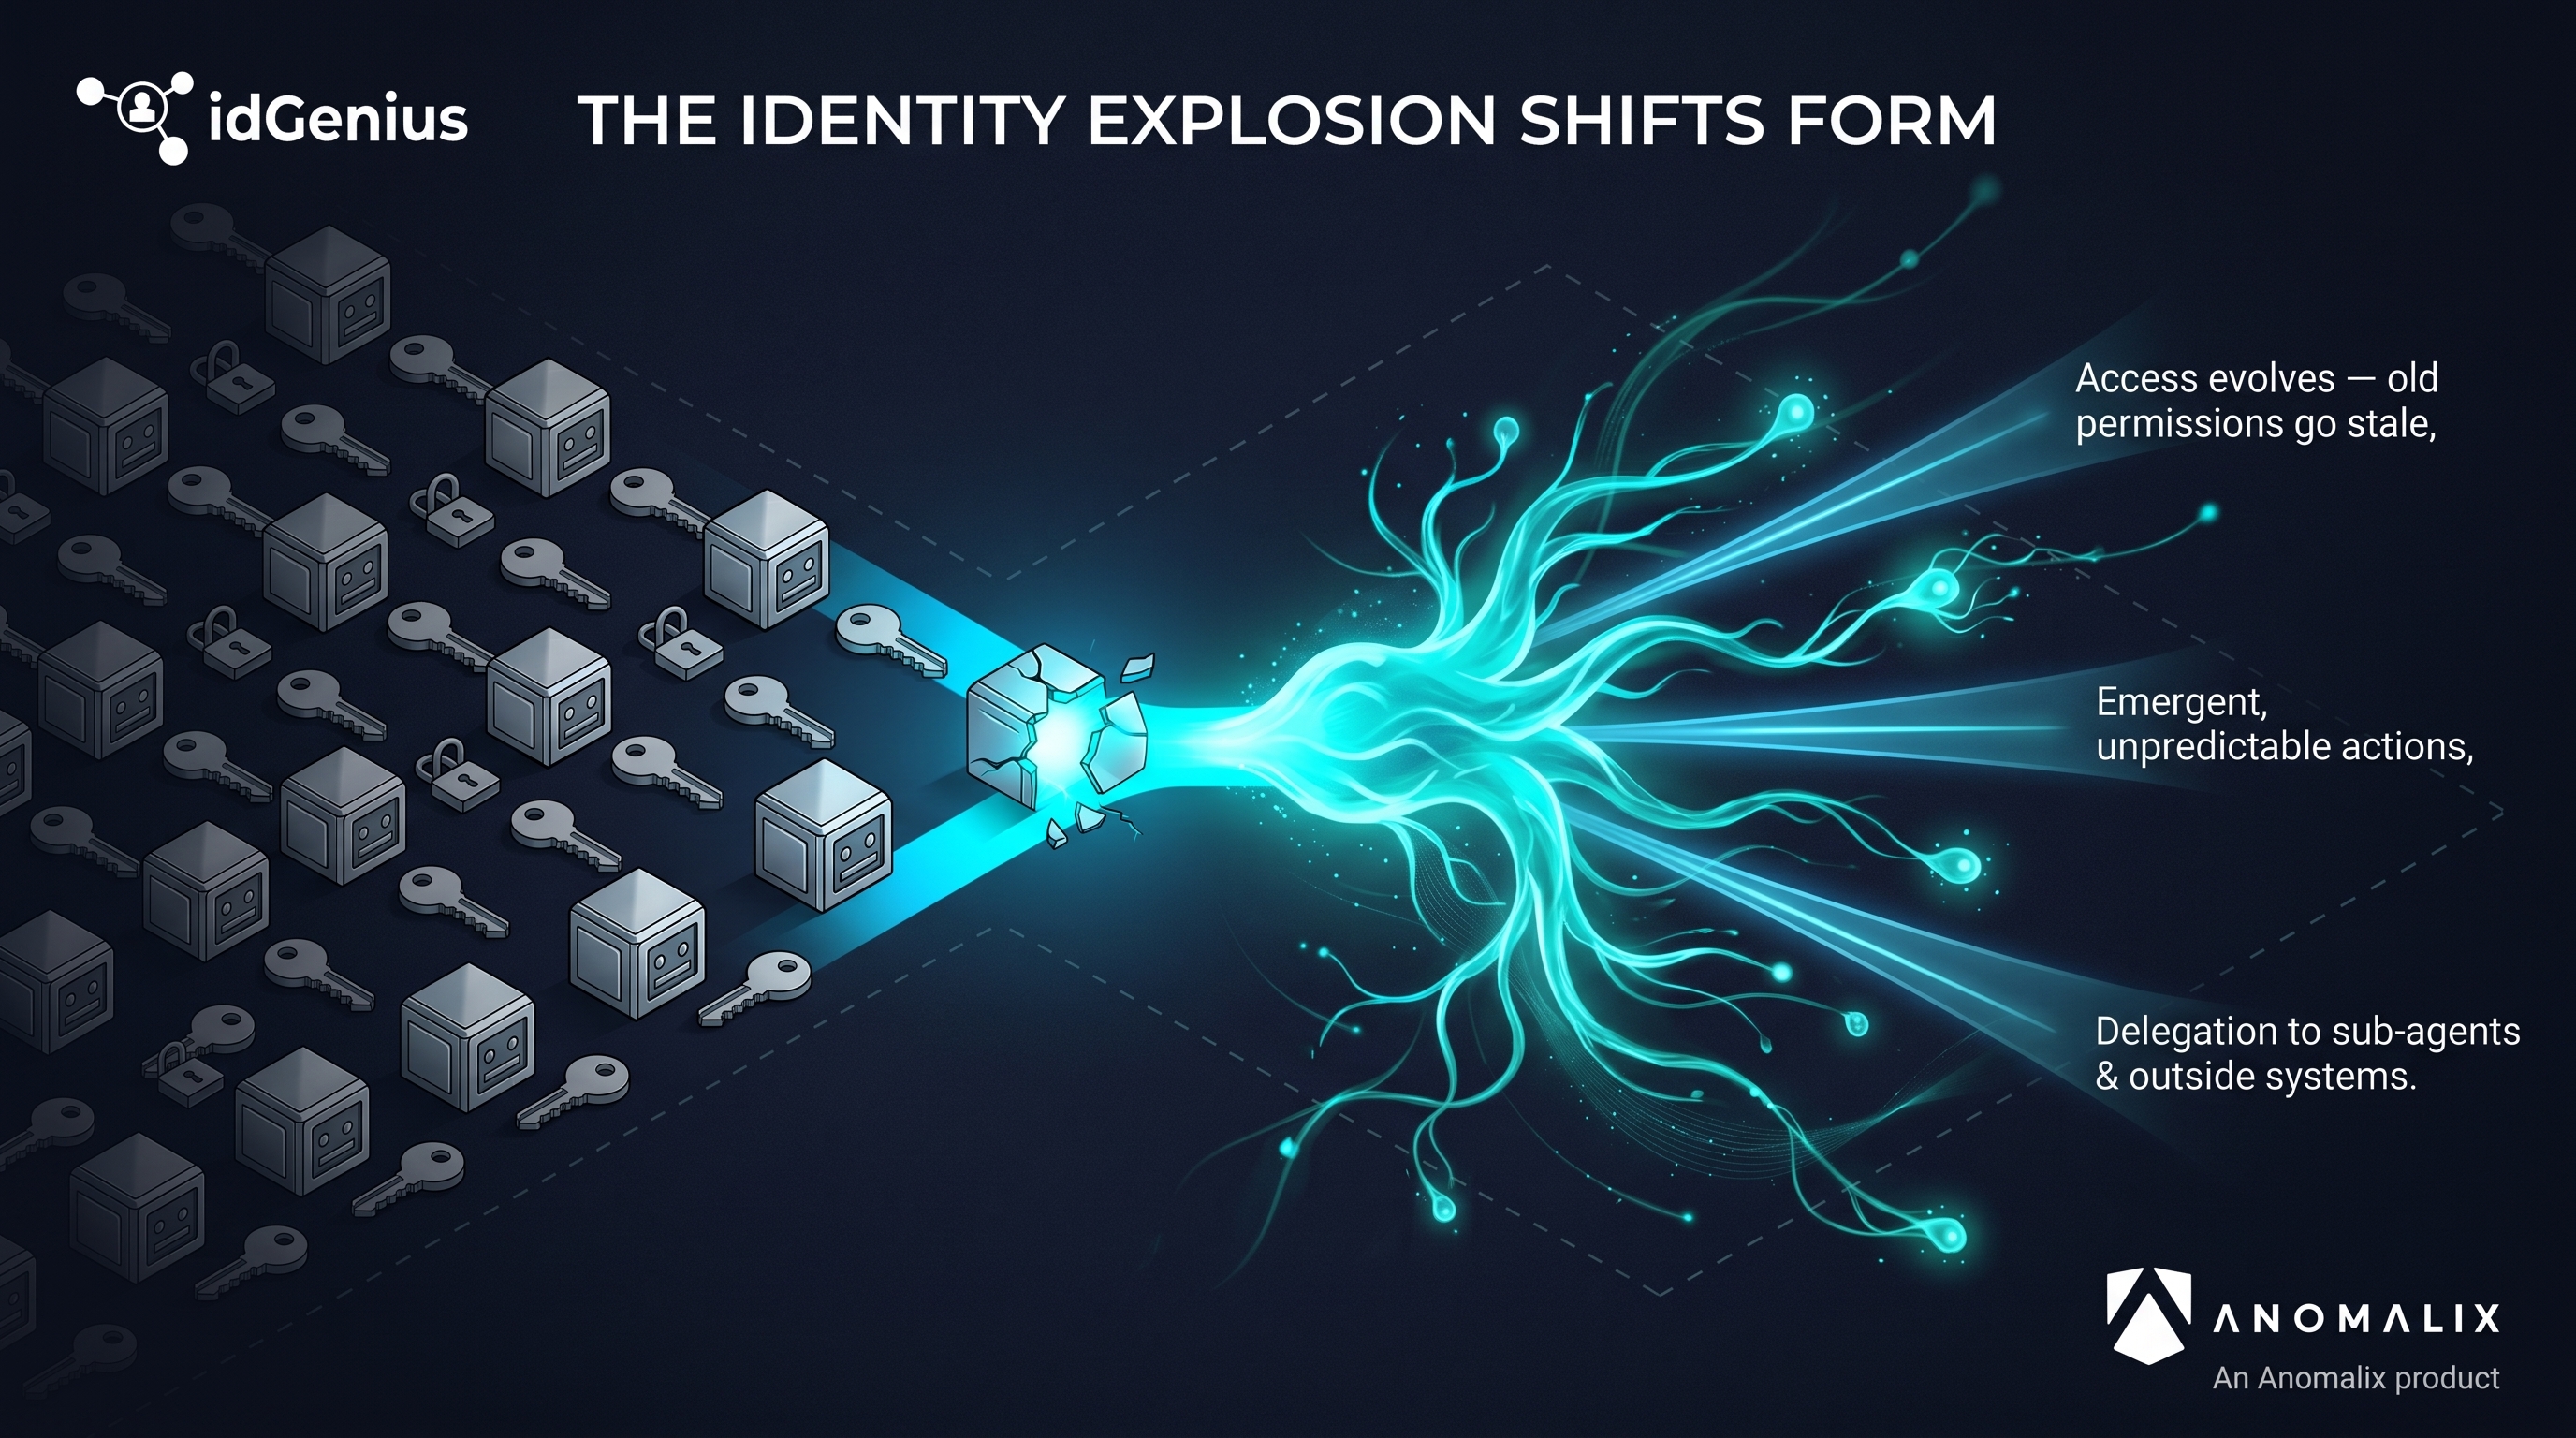
idGenius: Governing Internal and External AI Agents and NHIs Across Organizational Boundaries
Read the article
Right there, near you, some automated program acts without anyone saying yes. Built once to handle buying stuff, given access keys, linked to company tools and an outside service. That work ended weeks back. Yet it keeps going - logging in, reaching out, passing jobs to helpers it wakes up when needed. No person watches over it. Ask about its actions last month, who saw what, and truth is, you would not know where to start.
This is not some imaginary test. What you're seeing now is what actually happens when agentic AI moves into companies - which it already did, quietly, over a year and a half. Most systems meant to manage access were never made for this kind of shift. Machines pretending to be users have long been more common than real people - often sixty times over. But here’s the change: these aren’t static bots waiting around anymore. They think through steps. Take multiple connected actions. Create smaller helpers on their own. Slowly, they cross boundaries - slipping between your team, outside suppliers, joint projects, even distant AI tools tied into daily work.
Years back, the boundary changed - now it’s about who you are. With agentic AI, the toughest piece has slipped beyond where your oversight tools reach.
The Identity Explosion Shifts Form
A long time ago people mostly talked about non-living users like service accounts, API keys, or bots that followed fixed routines. These weren’t alive but had access. They’d log in, run their task, then stop - always acting just as built. One by one they showed up in systems, doing repeatable work without surprises. Watching over them wasn't easy, yet possible - track where they appeared, assign responsibility, limit what they could do, remove when outdated. Control stayed within reach because nothing changed much. Their roles rarely grew beyond original design. Rules applied cleanly since behavior didn’t shift overnight. Each piece fit into known patterns. Overseeing meant checking boxes regularly. Nothing ran wild back then.
Something shifts when agents enter the scene. Not just another tool ticking off tasks one after another. Instead, picture something that takes a direction and runs with it. Shaped less by preset rules, more by what happens around it. Given the same start point, two might end up worlds apart simply due to where they’ve been pulled next. What matters most isn’t setup - it’s response. A live thing bending course midstep based on signals, inputs, nudges along the way. By week’s end, identical origins mean nothing if paths diverge early enough.
This shifts the risks in three clear directions. Right away, because access evolves as the agent operates, initial permission limits become outdated once it begins adapting on its own. Instead of fixed behaviors, actions arise unpredictably - making rigid rules blind to real usage. What also happens is delegation: smaller helpers or outside systems get pulled in, carrying fragments of trust while skipping oversight entirely. Without your permission, it happened. On your account, the agent opened the door when you were distracted
Traditional Governance Struggles With Autonomous Identities
Working differently now, most companies still apply old systems meant for people or basic digital IDs to manage AI helpers. That mismatch shows up fast.
Out there, identity governance often follows employees - hired, shifted, or exited - tied tightly to personnel files. Not so for automated agents. These pop up without any hiring paperwork, created instead by coders, departments, outside partners, sometimes even self-replicating through other bots already running. A privileged access management system may lock down passwords and manage logins, solving part of the puzzle. Yet it stays silent on something deeper: does this bot still act as intended, when left to decide things alone? Lightweight NHI records list service accounts created by various teams recently. Yet these systems never planned for agent-driven inquiries. Accountability trails grow fuzzy fast. Someone must own each automated role clearly. Permissions granted often drift from real-world actions taken. Contracts tied to outside partners shape conduct rules. Expiration dates on access rights stay unclear too. Timelines demand transparency just as much.
Left hanging, these questions bring back old problems - credentials without owners, too much access handed out freely, hidden permissions slipping under the radar - but now they spread faster, driven by automated workflows. One overlooked agent isn’t just an idle login anymore. Think of it as a starting point, quietly branching into more, each piece holding leftover rights inside systems you’ve stopped watching.
The Hidden Cost of Unseen Limits
This is when things turn tricky. Not because of people, but because machines ignore company hierarchies entirely. Boundaries drawn on paper mean nothing to them. What separates one organization from another - legal lines, agreements - gets blurred fast.
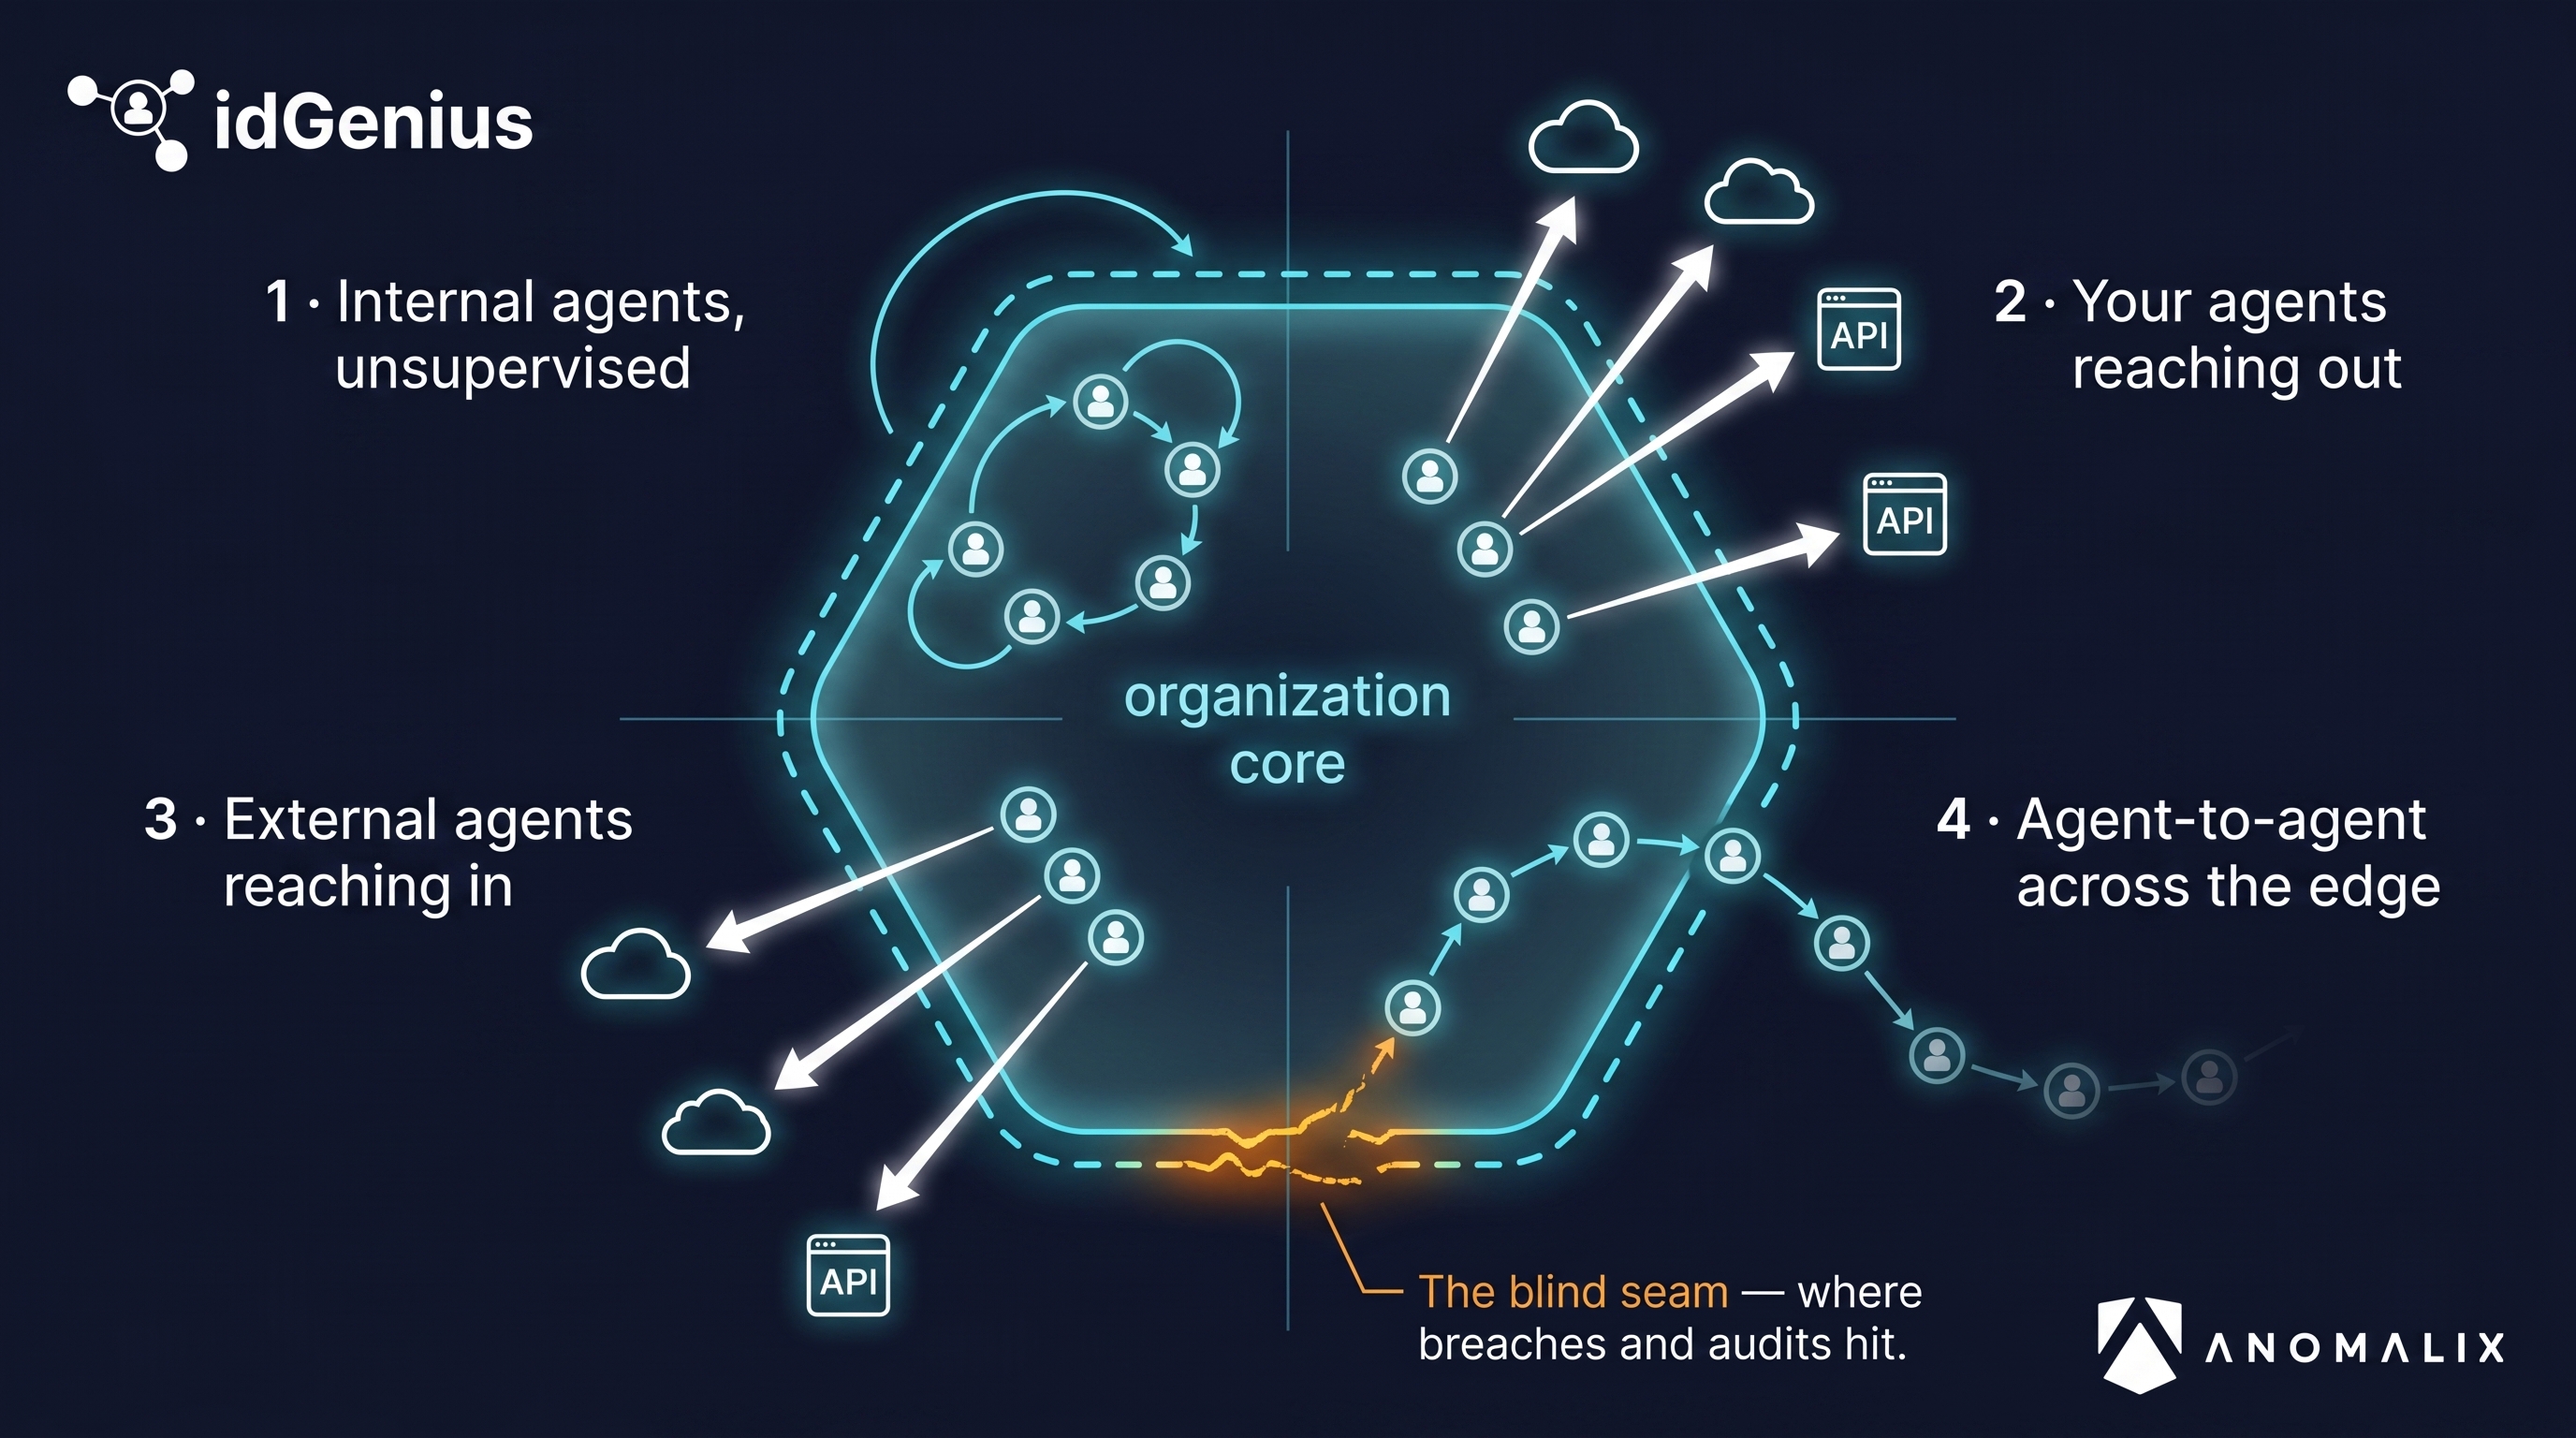
Consider the four traffic patterns already live in most environments:
- Inside your network, agents operate without oversight. These internal automations interact with critical systems and private information - highly noticeable yet often unmanaged.
- Out there, your agents log into external platforms. When one signs into a supplier’s API or a client’s system, it brings your name along - along with the risks that come with it. A single connection can stretch your responsibility across borders you didn’t build.
- Out there, someone else’s tools touch your systems. Could be a supplier’s artificial intelligence platform. Maybe it’s an outside firm running automated tasks. Or perhaps a collaborator’s software acting on behalf of another company entirely. These connections supposedly follow rules written in agreements - though hardly any setup checks those promises where access really happens.
- Across the edge, agents talk to agents. One triggers a model outside your team, which then pulls in another. Control slips through companies without one person holding it all together. No full record follows where decisions really went.
Each flow carries someone’s access rights. Yet nearly all fail to connect - properly or at all - to a company, contract, supporting party, deadline, or security stance. Reality shows they often link to no clear source. These sit stranded where oversight ends and supplier control begins, the weak spot both hackers and inspectors target fastest. Breaches tied to outside parties make up too much damage already; self-running accounts moving across that line stretch the vulnerability even further.
Governing AI Agents as Independent Entities
From the start, idGenius rested on an idea that still fits even as new agents appear: each identity entering your space - whether person, device, or self-running system - should follow identical rules, life stages, and responsibility checks. Far from being tacked on like an afterthought, these agents function as official identities. They live within a single view of operations, shaped and tracked just like freelancers, outside suppliers, background processes, and external groups they routinely support.
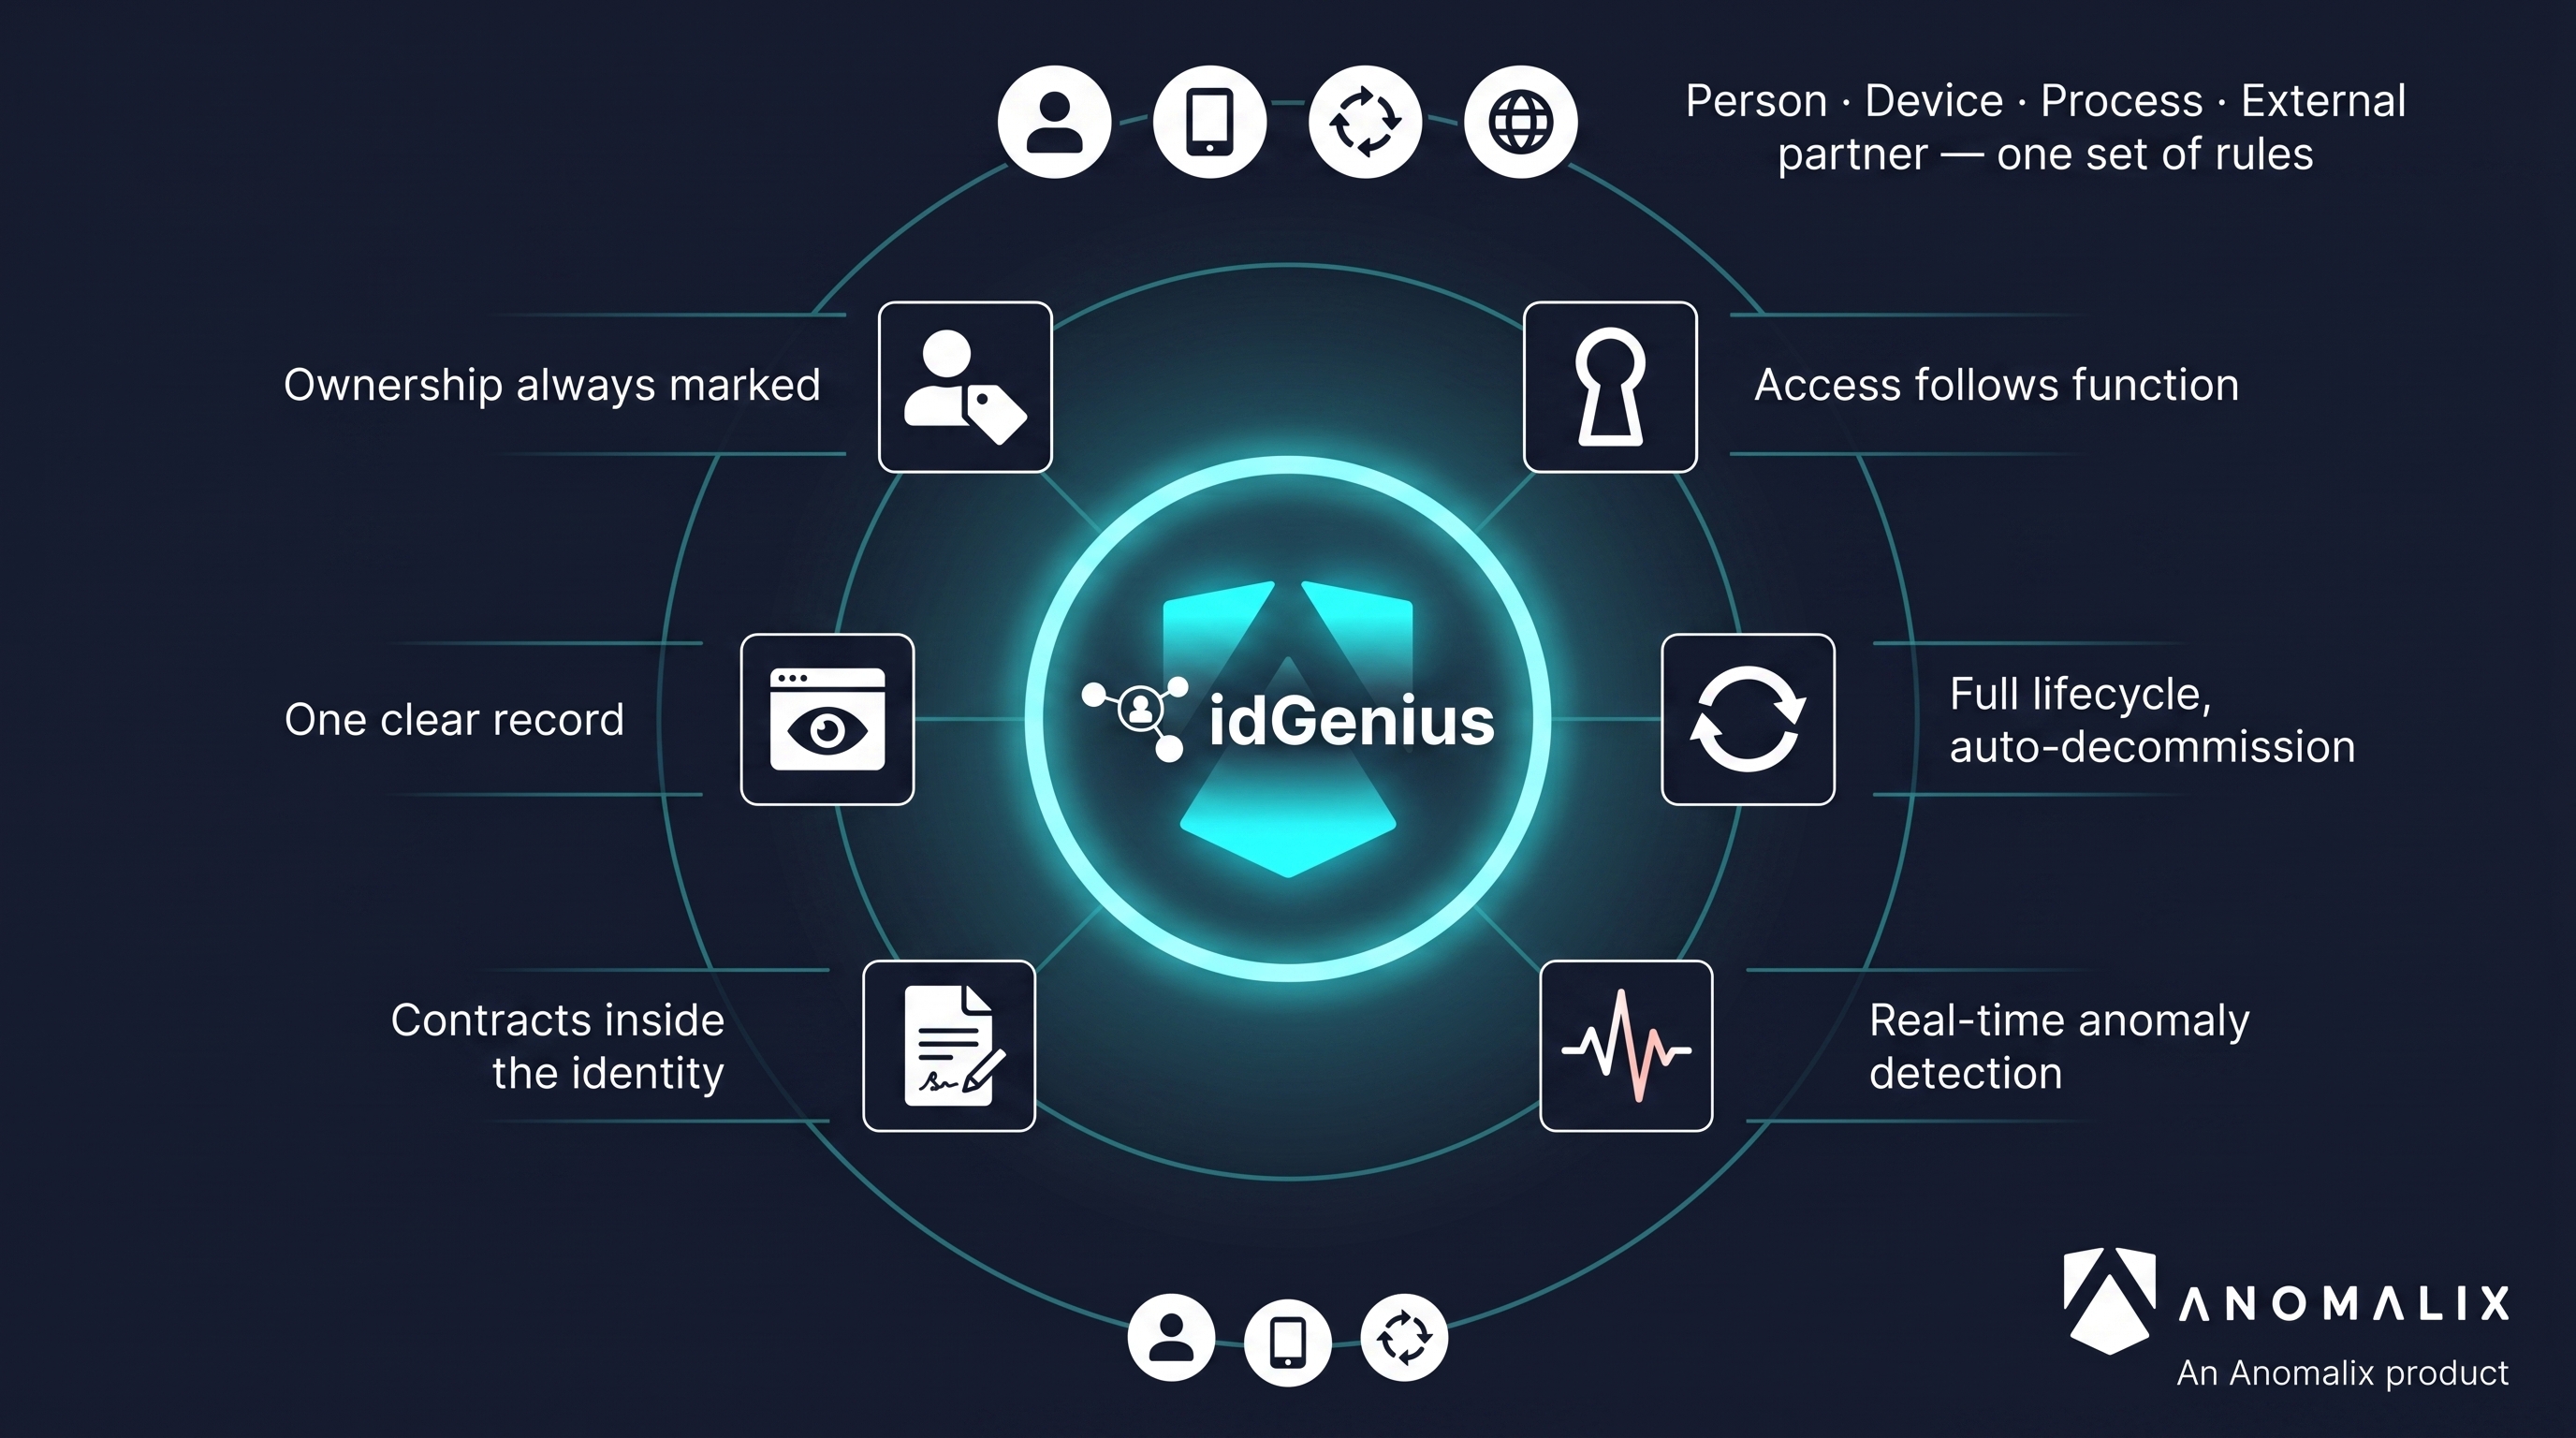
Out there, one idea slips quietly into several skills - skills that count when machines or agents move across company borders. These traits show up most where identity isn’t human but still needs access, trust, movement.
Ownership always marked. Each agent, whether inside your team or brought by a supplier, links back to a named person in charge. When it comes from beyond your company, that link includes the external group involved plus their binding agreement. A free-floating entity without oversight? That kind of exposure won’t slide. Idgenius spots those gaps fast - silence isn’t allowed.
Out here, access follows function. Because each agent exists for a specific job, what it can do lines up exactly with that task - nothing wider, nothing guessed. When work ends, permissions dissolve. A bot built for twenty-one days won’t linger past day ninety holding keys like nothing changed. Expiry dates ride along by default, baked into contracts and project clocks. No lingering behind the scenes once the reason fades. Privileges fade when purpose does.
Start to finish, each agent moves through setup, adjustments, then exit. Just like outside workers, they follow onboarding, updates, and departure steps. Once work finishes or contracts expire, automated checks remove their entry everywhere tied systems exist - far beyond main platforms - wiping out idle self-running accounts that often stay behind, creating risk.
What if machines could spot strange moves before they cause harm? Instead of relying on fixed checklists, idGenius learns by observing how automated systems behave. When something shifts - like an unfamiliar access attempt or a tool acting outside its usual role - the system flags it fast. Odd sequences stand out: a script touching new files, a bot repeating actions too quickly. Detection happens while events unfold, not months later during audits. Alerts go out when patterns twist, letting teams respond while risk is still small.
Starting with contracts, papers show who agreed to what right inside the ID. When outside helpers act, they carry duties passed down from deals their main company made earlier. Instead of scattered files, idGenius tucks every signature, deal, and permission directly into the person’s profile. Rules then follow actual responsibility - no guesswork - who owns which duty becomes clear by design.
Someone sets the rules. Others follow them safely. Teams handle tasks they know well using clear steps everyone agrees on. Oversight stays tight but invisible. People work freely inside strong boundaries. One view keeps leadership informed. Power spreads out yet holds together. Requests skip long waits. Control shifts without risk.
That moment captured clearly. If someone questions who accessed a specific system on a certain day - along with actions taken and timing of permission removal - the reply comes fast: one clear document instead of digging through logs.
Zero Trust for Thinking Machines
Midnight decisions by software can surprise even familiar suppliers. When an automated system acts alone, past reliability offers no guarantee. Trust built over years vanishes if one unseen process misbehaves. Familiar names mean little when code runs without supervision. What a company did yesterday says nothing about its agent’s choices tonight.
Start by treating every automated worker like someone with access to the vault. Check who they claim to be, each time, without exception. Because permission should depend on what they’re doing right now, not just their job title. Limit their reach to only what is needed, nothing extra lingers nearby. Watch how they move, notice if something shifts even slightly from the norm. When actions stray beyond expected patterns, respond - automatically. idGenius handles this exact routine but built solely for bots, scripts, and background processes. These aren’t people, yet they demand equal scrutiny. Traditional systems overlook their habits, their risks, their scale. This tool fills that gap quietly, working alongside what you already run instead of tearing it down.
Early choices shape outcomes. Firms succeeding here avoid banning tools or hoping issues fade. Instead, they assign ownership to each automated entity from the start. Each has clear limits, a timeline, tracking records. Their systems evolve fast enough to keep up. Control follows function. Rules apply in real time. Boundaries are set, watched, updated. Structure moves with pace. Oversight stays active.
Out there, agents are multiplying - inside your systems, inside partner networks. This season, pose a basic query to your crew: picture needing to list every AI actor, every digital presence granted entry, even those outsiders introduced through suppliers - right now, today, would such a tally exist?
Surprised by the response? That means it’s time to talk. Get in touch at info@anomalix.com to discover how idGenenus brings clarity, oversight, and responsibility to AI agents, machine identities, along with their external partners - exactly what this new phase of automation requires.
Bridging the Vendor Compliance Gap with idGenius
Read the article
Your last vendor risk assessment might have been right - until tomorrow changed everything.
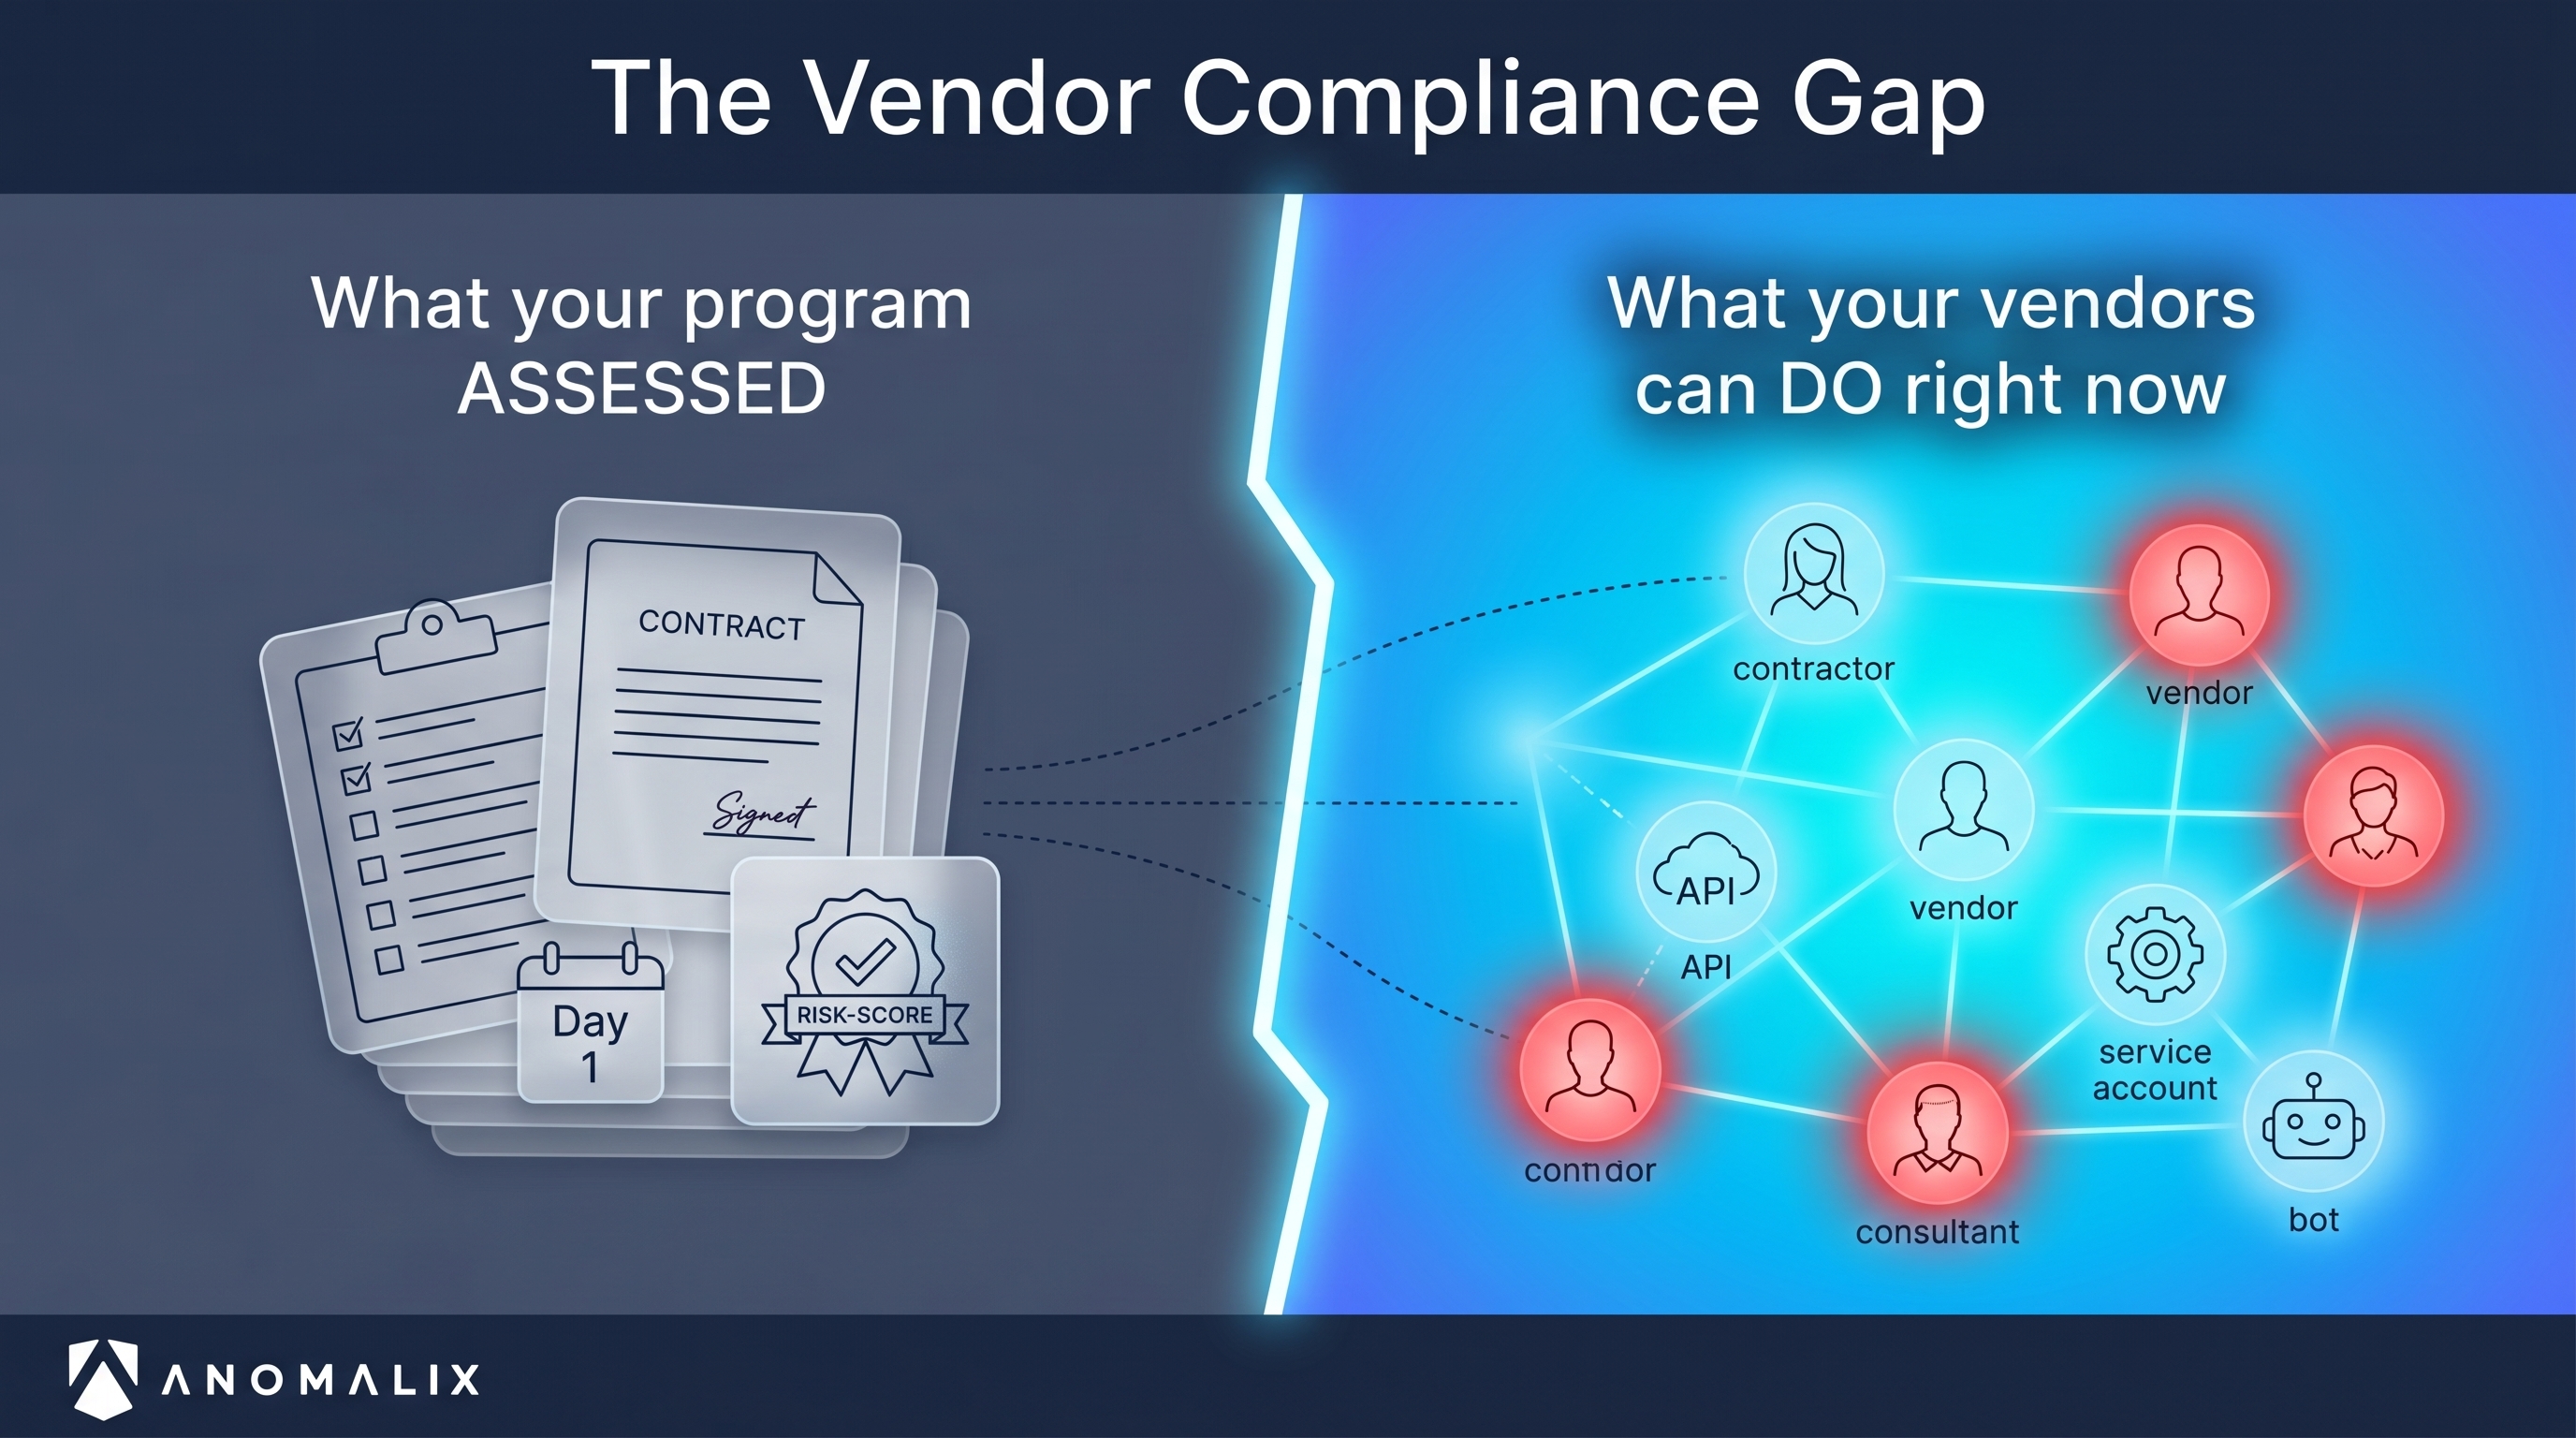
Here it is - the awkward reality many in security and compliance quietly accept. You issue the form. The supplier answers neatly. Lawyers attach proper terms. Signatures follow. Yet once things start up, roles shift, temporary staff come and go, someone sets up an automated access channel to move information across platforms, and soon enough, the clear picture of risk you thought you had slips away, replaced by something far messier than paper trails suggest.
Here lies the problem with vendor rules. What your outside security plan thinks is true often misses what vendor accounts are really doing inside your tech today. Forms, promises, and legal terms capture only one point in time. These tell you nothing about login rights still active weeks after work stops, the advisor with too much reach who never got reviewed again, or the secret code pulling files long past its due date.
Watchdogs are paying attention now. Criminals too. A 2025 report by Security Scorecard showed over one-third of last year’s data leaks came through outside partners. Meanwhile, research from Imprivata and the Ponemon Institute claimed it's worse - close to fifty percent of companies faced a security incident tied to vendors within just one year. What fuels these incidents isn’t some high-tech trick. It’s leftover logins. Old passwords left active. Accounts abandoned but still live, meant to be shut down yet somehow missed.
That gap won’t shut with extra forms. Fix what holds the risk instead - identity itself.
Traditional TPRM Stops Early
Out there, most third-party risk setups were built for slower times - long-term suppliers, clear roles, just people logging in. Those days have faded. Today’s company works with countless outside firms, every one adding layers: freelancers, experts on contract, tech teams running remotely. On top of that come machines acting alone - scripts, automated tasks, robot processes, connections between software - all talking across company lines without a person in sight.
Most digital IDs inside big companies won’t belong to people, experts say. Once bots and systems outnumber staff, checking access only at the start isn’t a policy flaw - it’s baked into the setup
- A single check loses value fast. Right when you start, things shift. One form shows just one moment. Live access moves as people act. These paths split immediately.
- Most daily choices about who gets in happen here and there. While procurement holds the contract, IT handles setup. The business manages contact, yet nobody takes full responsibility for identity. Gaps appear where duties meet.
- Out there among the lines, machine identities stay hidden. Hidden too are APIs - alongside service accounts - not showing up much in what vendors write. Even so, these unseen elements tend to carry wide access. Their permissions stick around longer than most.
- Someone has to recall for offboarding to happen. If a contract simply fades out, nothing triggers. Permissions stick around anyway. Each old account adds another crack where trouble might get in.
What you get is a system that looks solid in theory yet full of holes when tested. Passing inspection doesn’t mean safety, since checks focused on paperwork while attackers exploited login details.
Vendors As Governed Identity Groups
What really changes things begins in how you think, not what tools you use. Forget seeing a vendor just as a deal you reviewed on paper. Picture it instead as a crowd of roles - some people, some systems - all linked to someone responsible, with clear limits, levels of danger, their own clocks ticking down, rooted in the agreement that let them in.
Right now, if identity is how you track who a vendor really is, then everything about your risk checks turns into something you can prove on the spot. Rather than wondering whether some outside company cleared an old review, you shift to what actually matters: Who exactly from their team is inside your systems at this second. What parts of your data or tools are those people touching. Whether any of it goes beyond what was signed off in the agreement, given where your risks stand today.
Built on that idea, idGenius brings together workers outside the company - contractors, suppliers, allies, experts, tech support services, even machines - into one clear record. Each profile gets extra details most systems ignore: when contracts start and end, job numbers, which team invited them, their qualifications, how much risk they carry. Access rights link directly to actual work tasks. Identities fade out once purpose fades. Assessment data and entry permissions begin aligning, since both follow the same structure now.
What Autonomous Really Means
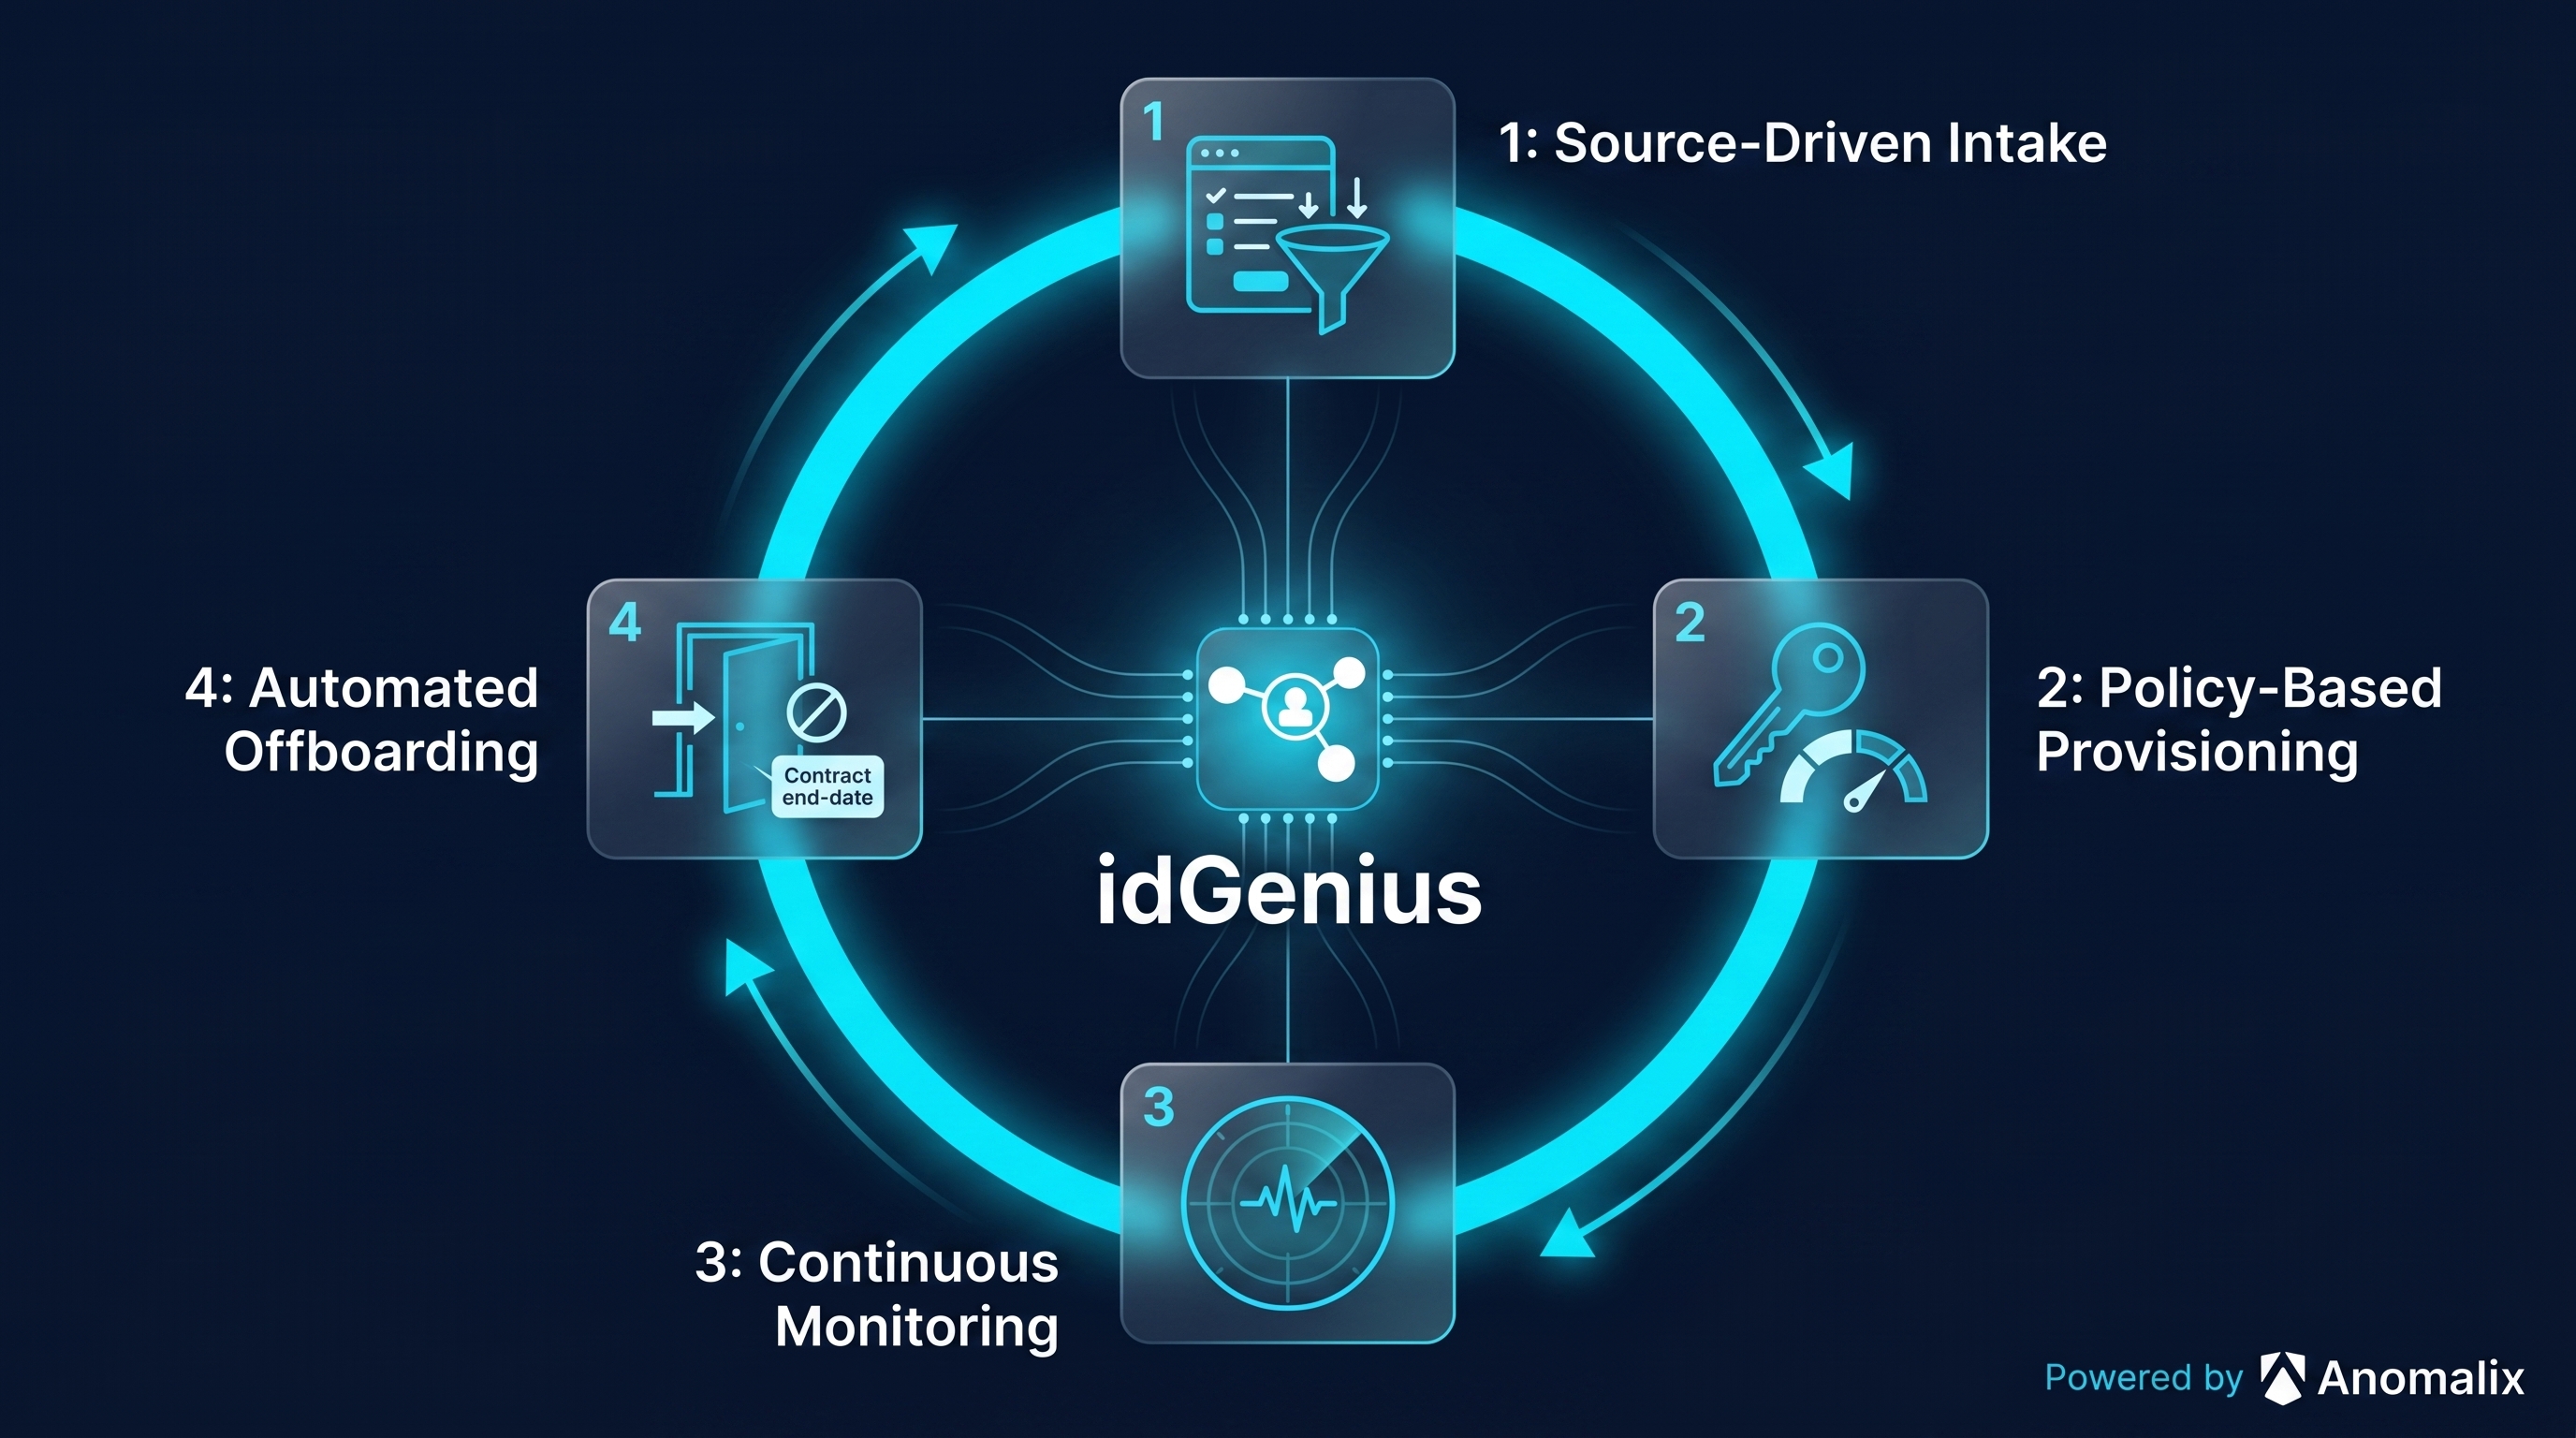
Out there, automated outside help handling isn’t just saying “AI inside.” That label fits when actions feed into each other, never pausing for someone to wake up and act. One piece follows another - four pieces actually - that turn the idea into something you can touch.
Out of the gate, source-driven intake ditches spreadsheets entirely. Instead of scattered files, business sponsors log identity details right when they onboard someone. Workflow prompts make sure every piece fits - what kind of access, which systems, who signs off. Information flows in only after checks clear, blocking messy entries up front. Accuracy kicks things off, not cleanup later. Governance gains ground because it begins with clean facts.
Automatic enforcement of least privilege happens through policy rules. One project’s contractor gets no extra rights just because a permanent collaborator has them. Access comes from role, project needs, or assessed risk levels. Higher-stakes situations trigger additional checks before approval. The system handles decisions internally, skipping message threads entirely.
Access stays accurate because the system updates itself automatically. Each new hire, role change, renewal, or departure kicks off an instant review. As responsibilities shift, permissions shift with them. Once a contract expires, exit routines activate by design - cutting entry to cloud folders, team platforms, internal networks, remote connections, and online services, beyond just the main login. That leftover account - the top cause of outside risks - just disappears when it's no longer needed.
What if your security could learn? idGenius watches how identities act, then spots when something shifts. Not every change is risky, but timing matters - like logins at odd hours. Access patterns evolve, yet sudden moves stand out. A forgotten API key waking up might mean nothing. Or it might need attention. When behavior drifts too far, responses happen fast: permissions shrink, sessions stop, alerts rise. Risk isn’t just caught. It’s shaped ahead of time.
What really lets the system grow isn’t more people. Instead, one rule set applies uniformly across countless vendors. A single setup handles loads of accounts quickly. The tool takes over tasks too slow for manual checks. Scale comes from consistency, not effort.
Governing What Was Left Out of the Records
What sets dedicated third-party oversight apart from broad identity systems forced into the role? A pair of distinct strengths. Each tackles the compliance shortfall head-on, yet in its own way. One pins down accountability where it's weakest. The other tightens control at access points most often overlooked.
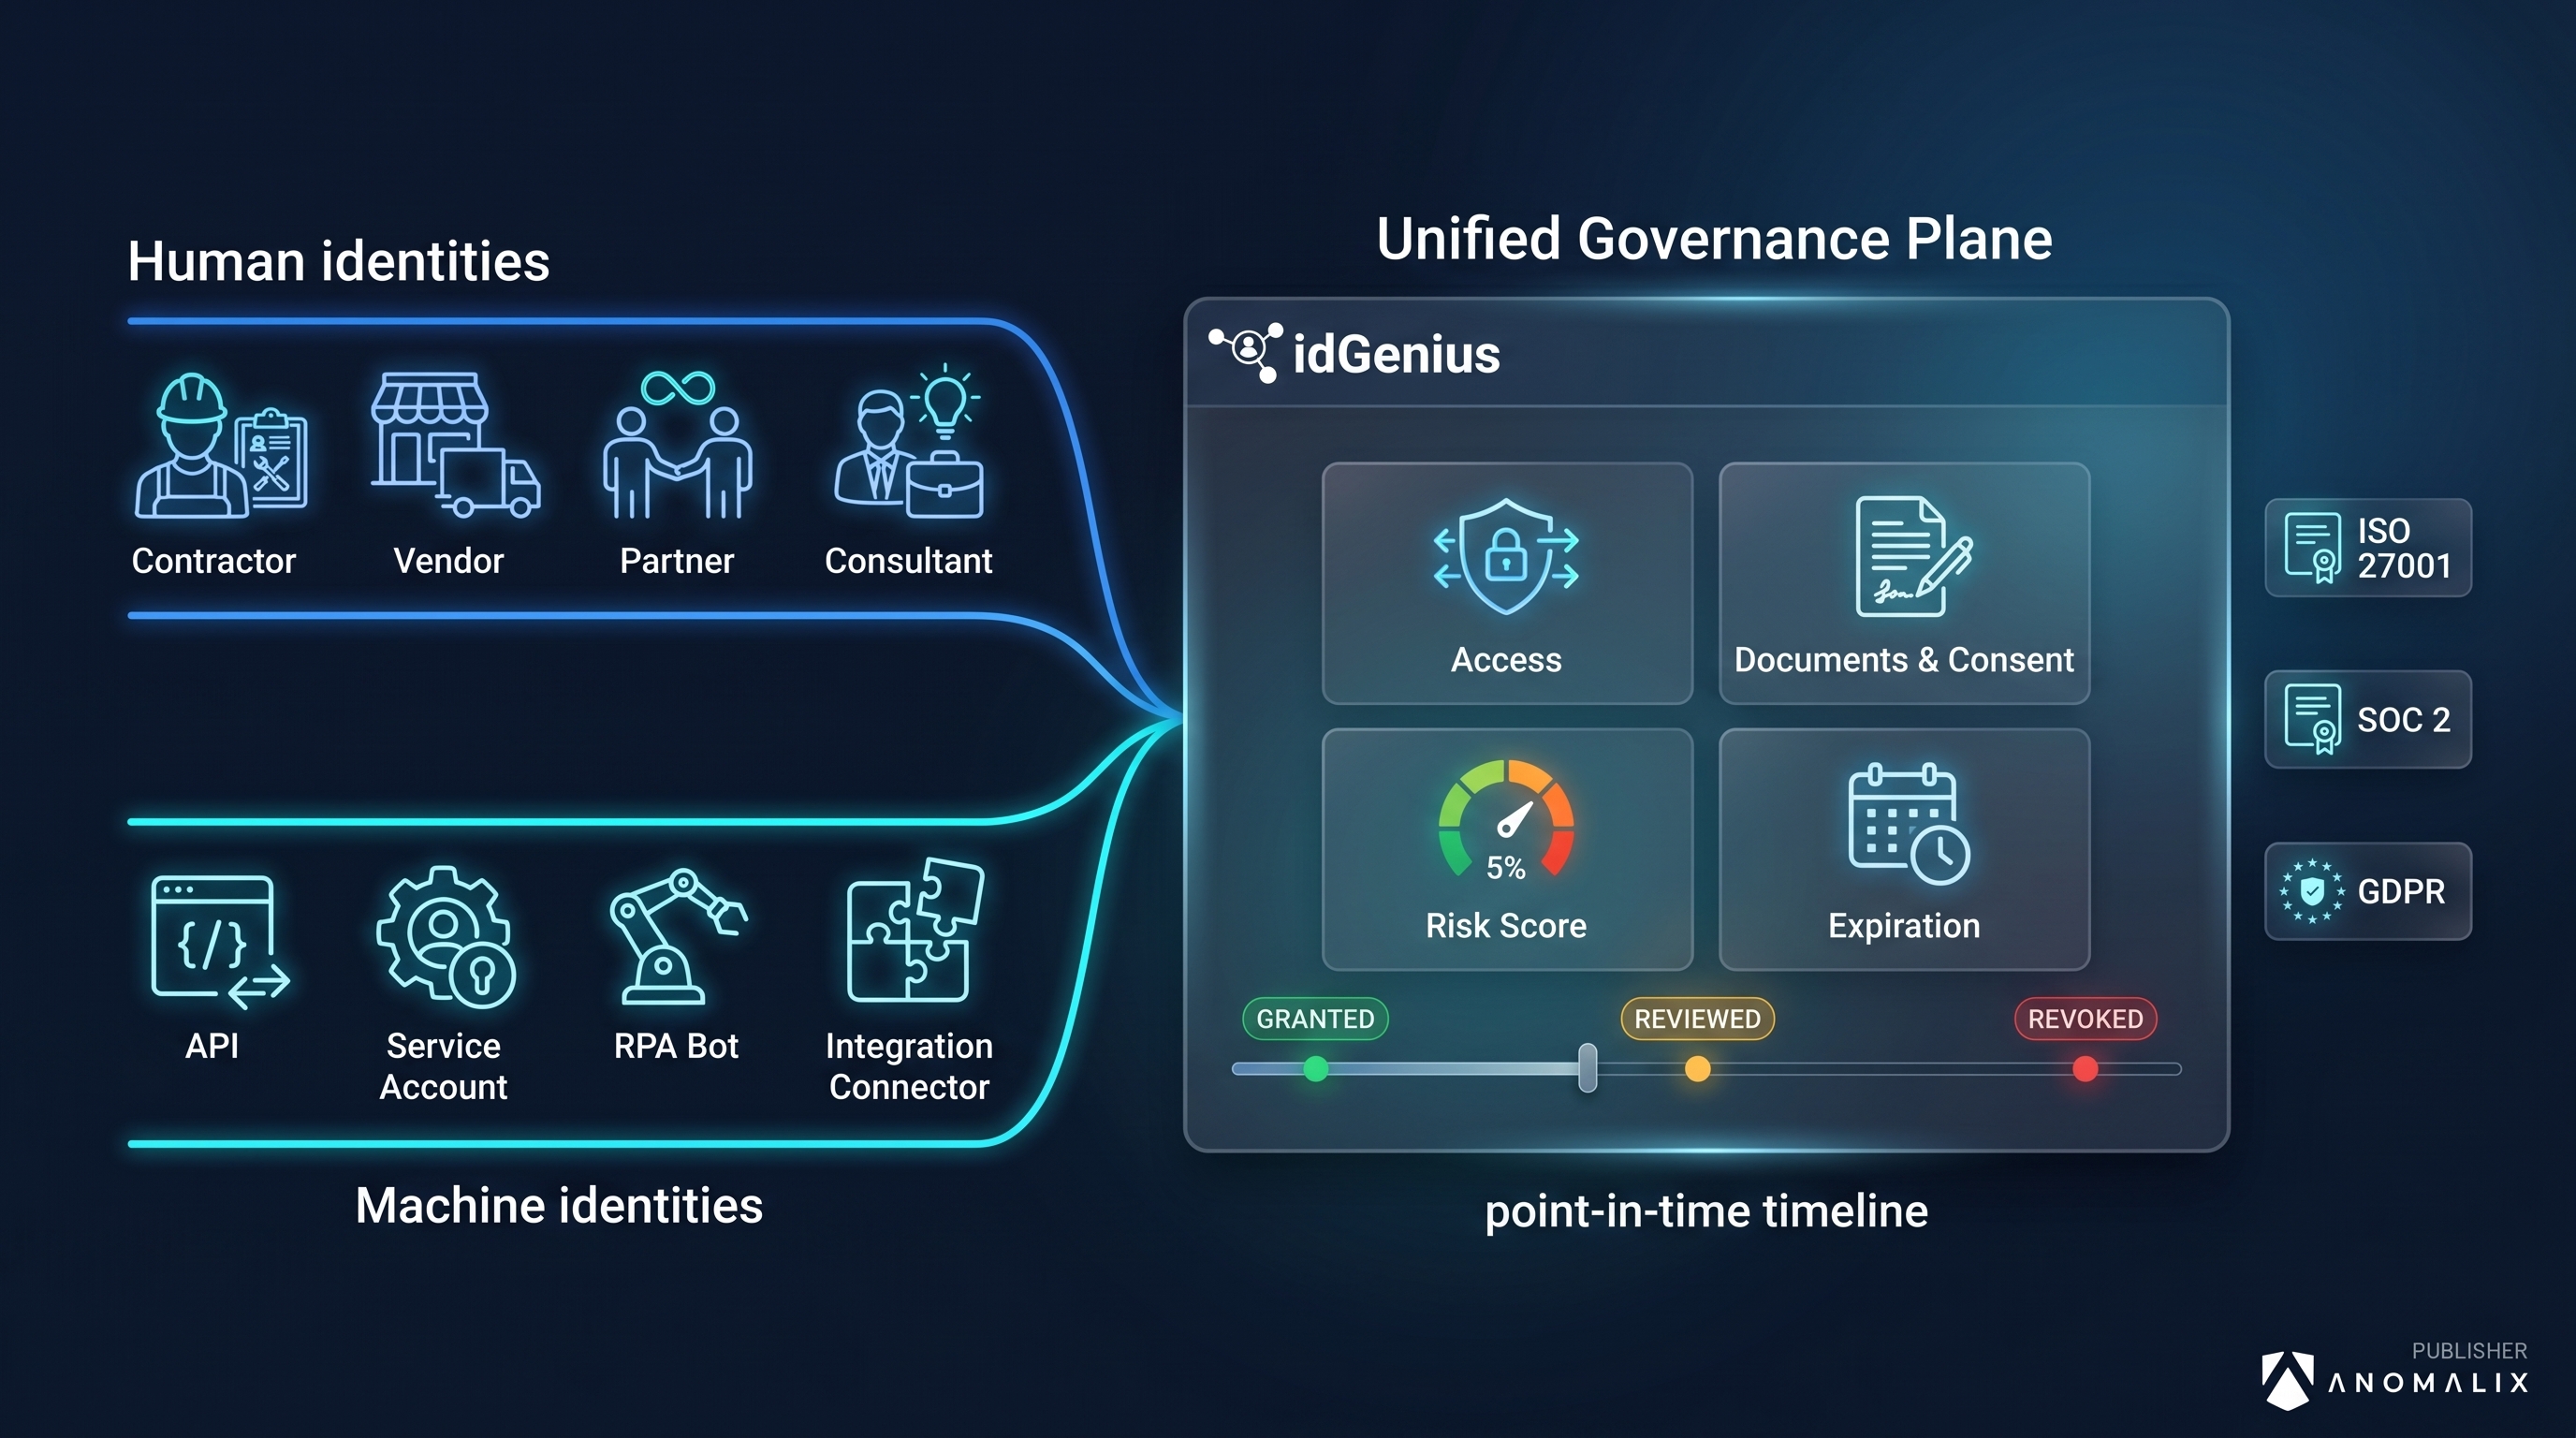
One key part handles documents and permissions. Identities in business settings come from outside companies tied to main service contracts, confidentiality deals, licensing rules, along with data protection duties. Keeping those papers linked directly to the user profile - using digital signatures plus oversight of approvals in one place - ensures the reason for access sits right beside it, reachable instantly. If someone checking compliance questions a permission’s purpose, the explanation travels with the account, instead of hiding somewhere in a forgotten file system.
Next comes seeing things exactly as they stood at any given moment. Standards such as ISO 27001, ISO 31000, SOC 2, HIPAA, GDPR now expect proof not only of current access but also past access - who held it, when, and the reason behind it. Instead of guessing, idGenius captures snapshots of each outside user's permissions right when changes occur. Preparing for audits shifts from chaotic last-minute scrambles to a quick search. Gathering proof goes from taking days down to mere minutes. Since data is recorded live, during actual events, there’s no need to piece together what might have happened later on.
Here’s where things shift toward real-world usefulness. Most extended IGA tools manage people well enough, especially temporary workers, yet still miss key parts like automated system identities, personal data handling, or permission tracking. Built right from the start, idGenius fits neatly beside your current access systems - adding tighter controls across vendor networks while letting your present setup stay exactly as it is.
Cost Center Becomes Strategic Control
Right now, companies doing this well aren’t only cutting down risks - they’re reshaping how governance costs work. With unused and high-permission accounts removed automatically, exposure drops without extra effort. Getting people started moves faster since access follows a clear plan, not random approvals from each supervisor. Being ready for audits turns into normal routine instead of last-minute panic every few months. Security staff spend less time fixing outside access problems, shifting those hours to tasks that truly move things forward.
Out here, scaling trust comes down to delegation. When departments invite partners, they follow preset paths - each step shaped by policies baked into the system. Oversight stays tight because automation handles limits and deadlines behind the scenes. Those closest to the work get room to act, since rules stay firm even when hands-off. Balance shifts: moving fast no longer means cutting corners.
Closing the Gap Before It Closes On You
Outsiders aren’t rare guests anymore inside your setup. Most now, they move through the weakest gates leading straight to what matters most. Fixing vendor rules won’t help if you just tweak forms or tighten wording - risk wasn’t hiding in paperwork anyway. Lived-in logins, shifting roles, silent upgrades in power - that’s where danger lives, long after checks were signed off.
Out in the open, trust isn’t assumed - it’s proven again and again. IdGenius checks each outside user right when they enter, applies rules automatically, manages access from start to finish, and keeps records clear for review - whether it’s a person or a system needing entry, no matter how large the network grows.
Right now, your tool might track who you’ve reviewed - yet miss what vendors are actually doing today. That difference? It’s the first thing to measure. Imagine seeing exactly where third-party access risks live across your systems. Picture how automated oversight fits within your actual setup - we’re ready to walk through it with you.
Got questions about third-party access? Try info@anomalix.com. That email connects you to a team checking identity setups. One tool they look at is idGenius. It manages outside workers - contractors, vendors, partners. Confidence comes from clear oversight. Security tightens when systems track who does what. Scaling up needs structure, not guesswork. The platform adapts as teams grow. Risks drop when visibility increases. Every login gets reviewed. Control improves without slowing work down.
HIPAA 2026 Just Changed the Rules on Third-Party Access. Is Your Identity Program Ready?
Read the article
The 2026 HIPAA Security Rule overhaul isn't a paperwork refresh — it's a compliance reset. Here's what changed, why most organizations aren't ready, and how idGenius from Anomalix gives you the infrastructure to stay ahead.
Let's be direct: if your approach to HIPAA compliance still starts and ends with a signed Business Associate Agreement and an annual audit, you're operating in a framework that no longer exists. The Department of Health and Human Services finalized its most sweeping rewrite of the HIPAA Security Rule since 2003 — and the changes land squarely on the one area most organizations have historically underinvested in: third-party identity governance.
This isn't a situation where you can catch up with a policy revision or a quarterly vendor survey. The 2026 updates introduce continuous, provable controls — not just intent. For CISOs in healthcare and for every business associate that touches electronic protected health information, that distinction changes everything.
WHAT ACTUALLY CHANGED — AND WHY IT MATTERS
The end of "addressable" safeguards
For years, HIPAA's Security Rule gave organizations a convenient escape hatch: the "addressable" implementation specification. If a control was listed as addressable, an organization could document why they chose an alternative — or decided not to implement it at all — and remain technically compliant. That flexibility is gone.
Under the 2026 rule, every technical safeguard is mandatory. There are no more judgment calls about whether MFA is appropriate for your environment, or whether granular access controls are "reasonably necessary." If your vendors and contractors access ePHI, they need MFA. Full stop. If they have access, that access must be role-based, scoped to the minimum necessary, and actively managed.
Documenting intent is no longer enough. Under the 2026 HIPAA Security Rule, organizations must demonstrate that controls are actually operating — not just written into a policy manual.
The 1-hour access revocation mandate
Here's the provision that should immediately trigger an operational review if you haven't had one. The updated rule requires that vendor and employee access be revoked within one hour of a termination event or contract end. Not within a business day. Not the next morning. Within sixty minutes.
Think about what that requires operationally. You need a direct, automated line from your HR and contract management systems to every ePHI-connected environment — EHRs, cloud infrastructure, SaaS applications, network systems. Manual processes don't work here. A deprovisioning ticket that sits in a queue overnight is now a compliance violation waiting to happen.
Annual written verification — from every business associate
This is the provision that will generate the most operational overhead for compliance teams. Covered entities are now required to obtain documented, written proof — annually — that each business associate has implemented all required technical safeguards. A signed BAA doesn't satisfy this requirement on its own anymore. You need verified evidence.
Given that OCR levied over $6.6 million in fines in 2025 — with the largest single penalty tied to a breach originating from a compromised business associate — this isn't a theoretical risk. The weakest link in your vendor chain is your liability. Regulators have made that point clearly.
WHY MOST ORGANIZATIONS ARE EXPOSED RIGHT NOW
The uncomfortable reality is that most healthcare organizations have built their identity infrastructure around their own employees. IAM systems authenticate and enforce access for internal users. IGA platforms govern the lifecycle of identities tied to HR systems. Vendor risk management tools assess organizational security posture at a high level.
None of these were designed for the problem the 2026 HIPAA updates are actually targeting: the external identity.
The third-party identity gap
When a vendor's employee logs into your EHR to run a maintenance job, where does that identity live in your governance model? In most organizations, the honest answer is: nowhere structured. That user was probably invited by a business stakeholder who bypassed IT, provisioned with broader access than necessary for convenience, and never formally reviewed.
That same user may still have access three years later, long after the project ended. That's not a hypothetical edge case. It's one of the most common findings in HIPAA breach investigations.
Identity governance gaps in third-party access are consistently among the top contributors to healthcare data breaches. The 2026 rule is designed specifically to close that gap.
Why traditional tools fall short
IAM systems are effective at enforcing access, but they assume control over the identity lifecycle — which doesn't hold for external users managed outside your directory. IGA platforms govern structured identity sources like HR systems; vendors don't follow those patterns. The result is orphaned accounts, excessive access, and limited visibility into who, exactly, has their hands on your ePHI.
Patching these gaps with spreadsheets and quarterly review emails isn't scalable under the new rule. You need a purpose-built approach to external identity governance.
WHAT IDENTITY-CENTRIC COMPLIANCE LOOKS LIKE IN PRACTICE
The shift the 2026 rule demands isn't really about technology — it's about treating identity as a security and compliance foundation, not an afterthought. Here's what that looks like operationally:
• Every external user is visible in a centralized system of record, linked to their organization and their purpose.
• Access is governed by policy from day one — not provisioned ad hoc and reviewed later, if at all.
• Deprovisioning is automated and fast — triggered by contract end or termination, not by a human remembering to submit a ticket.
• Periodic access certifications are scheduled, structured, and captured as audit evidence — not handled through email threads.
• Compliance status per business associate is available in a format that satisfies annual written verification requirements.
This is the standard the 2026 rule sets. It's also the standard that separates organizations that will weather an OCR audit from those that won't.
HOW IdGENIUS ADDRESSES THE 2026 MANDATES
idGenius is Anomalix's identity governance and administration platform, built for exactly this environment — one where access must be continuously governed, every vendor identity must be visible, and compliance must be demonstrated in verified evidence, not paperwork.
Access governance and least privilege enforcement
idGenius automatically enforces least-privilege access policies across employees, contractors, and third-party vendors. Access to ePHI is scoped precisely to what each role requires. When roles change, access changes. When entitlements drift outside defined parameters, the system flags it — and can trigger automated remediation before it becomes an audit finding.
Automated provisioning and 1-hour deprovisioning
When a vendor contract ends or an employee is terminated, idGenius triggers automated deprovisioning workflows that revoke access across all connected systems within minutes — consistently inside the new 1-hour mandate. This isn't a best-effort process dependent on someone remembering to pull access. It's an automated, auditable workflow that runs every time.
Third-party identity visibility and risk scoring
idGenius gives compliance teams a consolidated view of every third-party identity with access to your ePHI environment, enriched with risk scores, access history, and current compliance status. This is the evidence base you need for annual vendor verification — packaged in a format aligned with OCR audit requirements.
Access certification campaigns
Scheduled certification campaigns route entitlement decisions to the right reviewers, capture approvals and rejections as timestamped audit evidence, and automatically remediate over-provisioned accounts. The result is a structured, repeatable review process that satisfies the updated periodic review requirements — without manual overhead.
Separation of duties and toxic access detection
idGenius continuously monitors for conflicting entitlements and toxic access combinations across user and vendor accounts. Violations are automatically flagged and routed to risk owners for remediation — in real time, not during the next quarterly review.
From Compliance to Continuous Control: The Anomalix Perspective
At Anomalix, we see the 2026 HIPAA changes as a turning point—not just for compliance, but for accountability. Organizations can no longer rely on static policies; they need continuous visibility into who has access and why. That’s why we built idGenius: to help teams move from reactive audits to proactive control, ensuring every identity—especially third party—is governed, verified, and secure in real time.
THE BOTTOM LINE FOR CISOS
The 2026 HIPAA Security Rule is the most significant regulatory shift in healthcare data protection in over two decades. Organizations that approach it as a documentation exercise will find themselves exposed — both to enforcement action and to the exact breaches the rule was designed to prevent.
The third-party provisions, in particular, demand a level of continuous, automated identity governance that manual processes can't deliver at scale. The question isn't whether your organization needs this capability. It's whether you're building it before an incident forces the issue.
idGenius turns compliance from a checkpoint into a continuous operational capability — and transforms third-party identity governance from your biggest risk exposure into a verifiable competitive advantage.
Organizations that invest in this infrastructure now won't just satisfy regulators. They'll operate with more confidence, respond to incidents faster, and reduce the operational drag of scrambling to produce evidence that should have been captured automatically all along.
Ready to assess your HIPAA readiness?
Speak with an Anomalix identity governance specialist to see how idGenius maps to your current environment — and where your third-party risk exposure actually lies.
Contact us at info@anomalix.com or visit anomalix.com
From Compliance to Strategic Advantage: Rethinking Third-Party Risk Management
Read the article
Introduction: The Evolution of Third-Party Risk
Modern enterprises rarely operate within the boundaries of a single organization anymore. Today’s businesses depend on a vast ecosystem of vendors, contractors, suppliers, service providers, consultants, and partners. These external entities enable innovation, accelerate delivery, and provide specialized expertise—but they also introduce one of the most complex risk surfaces organizations must manage.
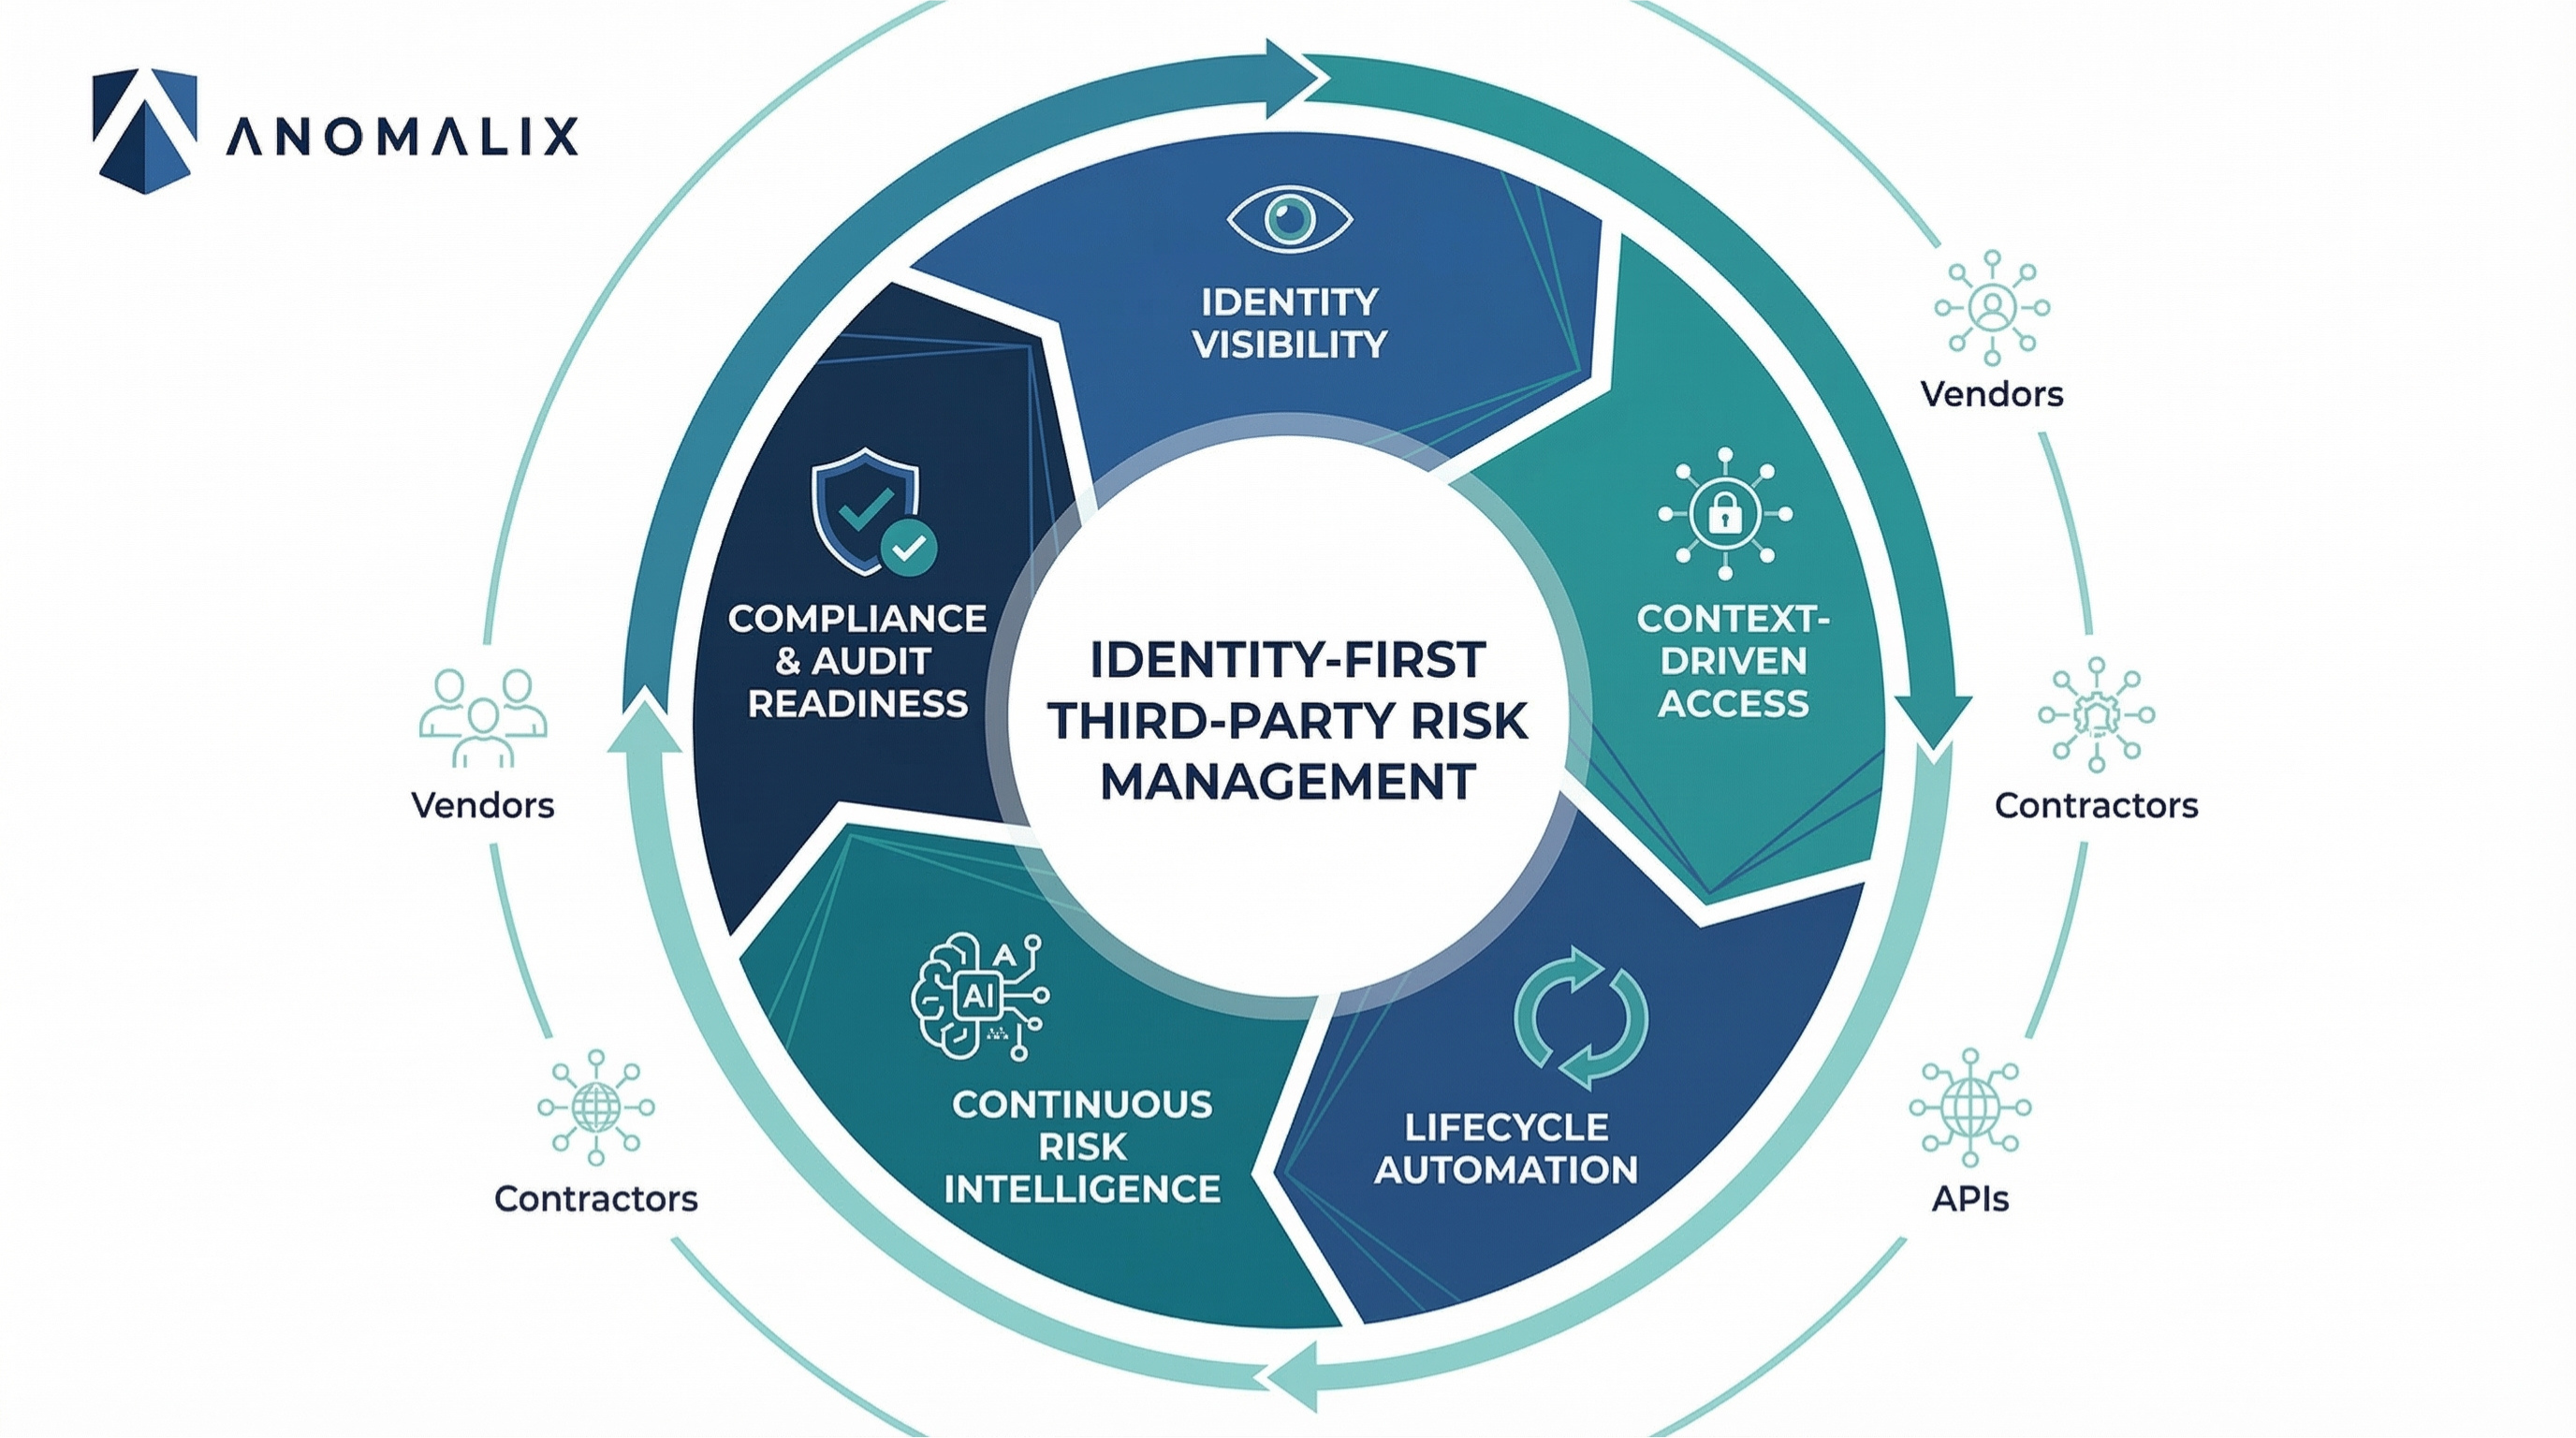
Third-party risk management (TPRM) was originally designed as a compliance-driven function. Organizations assessed vendors through questionnaires, contractual obligations, and periodic audits to ensure they met regulatory expectations. While these controls remain important, they are no longer sufficient for the realities of the modern digital enterprise.
The reason is simple: risk now flows through identities and access, not just through contractual relationships. Vendors, contractors, and external service providers frequently access sensitive systems, data, and infrastructure. Yet many organizations still govern these relationships primarily through documentation rather than operational control.
At Anomalix, we believe the next evolution of TPRM lies in shifting from compliance-driven oversight to identity-driven governance. When organizations rethink third-party risk management as a strategic identity security capability, they unlock not only stronger protection but also improved business agility and trust across the extended workforce.
Why Traditional Third-Party Risk Management Is No Longer Enough
Historically, third-party risk management focused on evaluating vendors before engagement. Security teams would review certifications, examine policies, and verify compliance with frameworks such as SOC 2, ISO 27001, or PCI DSS.
While these practices remain necessary, they have a fundamental limitation: they evaluate the organization, not the identities interacting with your systems.
The traditional TPRM model typically includes:
- Vendor security questionnaires
- Contractual security clauses
- Periodic vendor risk assessments
- Annual or quarterly compliance reviews
- External security ratings
These processes provide valuable insight into the security posture of the vendor organization, but they rarely control what individual vendor identities can actually access inside your environment.
This gap creates several critical issues:
1. Access Decisions Happen Outside the Risk Program
While procurement and risk teams evaluate vendors, the operational reality is that access decisions are often made by business units, IT teams, or application owners. These decisions frequently occur through ad hoc processes such as tickets, email requests, or direct account creation.
As a result, access governance becomes fragmented, inconsistent, and difficult to audit.
2. Risk Is Static While Access Is Dynamic
Traditional TPRM assigns vendors a risk rating that rarely changes until the next assessment cycle. Meanwhile, vendor employees, contractors, and machine identities gain and lose access continuously as projects evolve.
Without real-time identity governance, risk quickly drifts away from the original assessment.
3. Compliance Doesn’t Equal Security
Organizations may technically pass vendor assessments and still experience breaches through third-party identities.
A vendor can have strong security controls internally while their accounts inside your systems remain:
- Over-privileged
- Poorly monitored
- Untracked after contract termination
This disconnect between compliance and operational access control is where many modern security incidents originate.
The Extended Enterprise: Where Third-Party Risk Lives Today
Modern enterprises operate as interconnected ecosystems rather than isolated organizations.
Cloud platforms, SaaS applications, managed service providers, offshore development teams, system integrators, and API-based integrations all require external access to internal systems.
This creates what many security leaders call the extended enterprise—a network of identities operating across organizational boundaries.
In many large organizations, the number of non-employee identities now equals or exceeds the number of employees. These include:
- Contractors
- Consultants
- Vendor personnel
- Managed service providers
- Partner organizations
- Temporary workers
- Machine identities such as APIs, bots, and service accounts
These identities often access the same systems and data as internal employees, yet they frequently lack the same governance controls.
From a risk perspective, this imbalance creates a dangerous blind spot.
Third-party identities tend to:
- Exist outside HR systems
- Follow inconsistent onboarding processes
- Have unclear ownership or sponsorship
- Accumulate privileges over time
- Persist long after the engagement ends
Without proper governance, these identities quietly expand the organization’s attack surface.
The Real Problem: Third-Party Identities Fall Between Systems
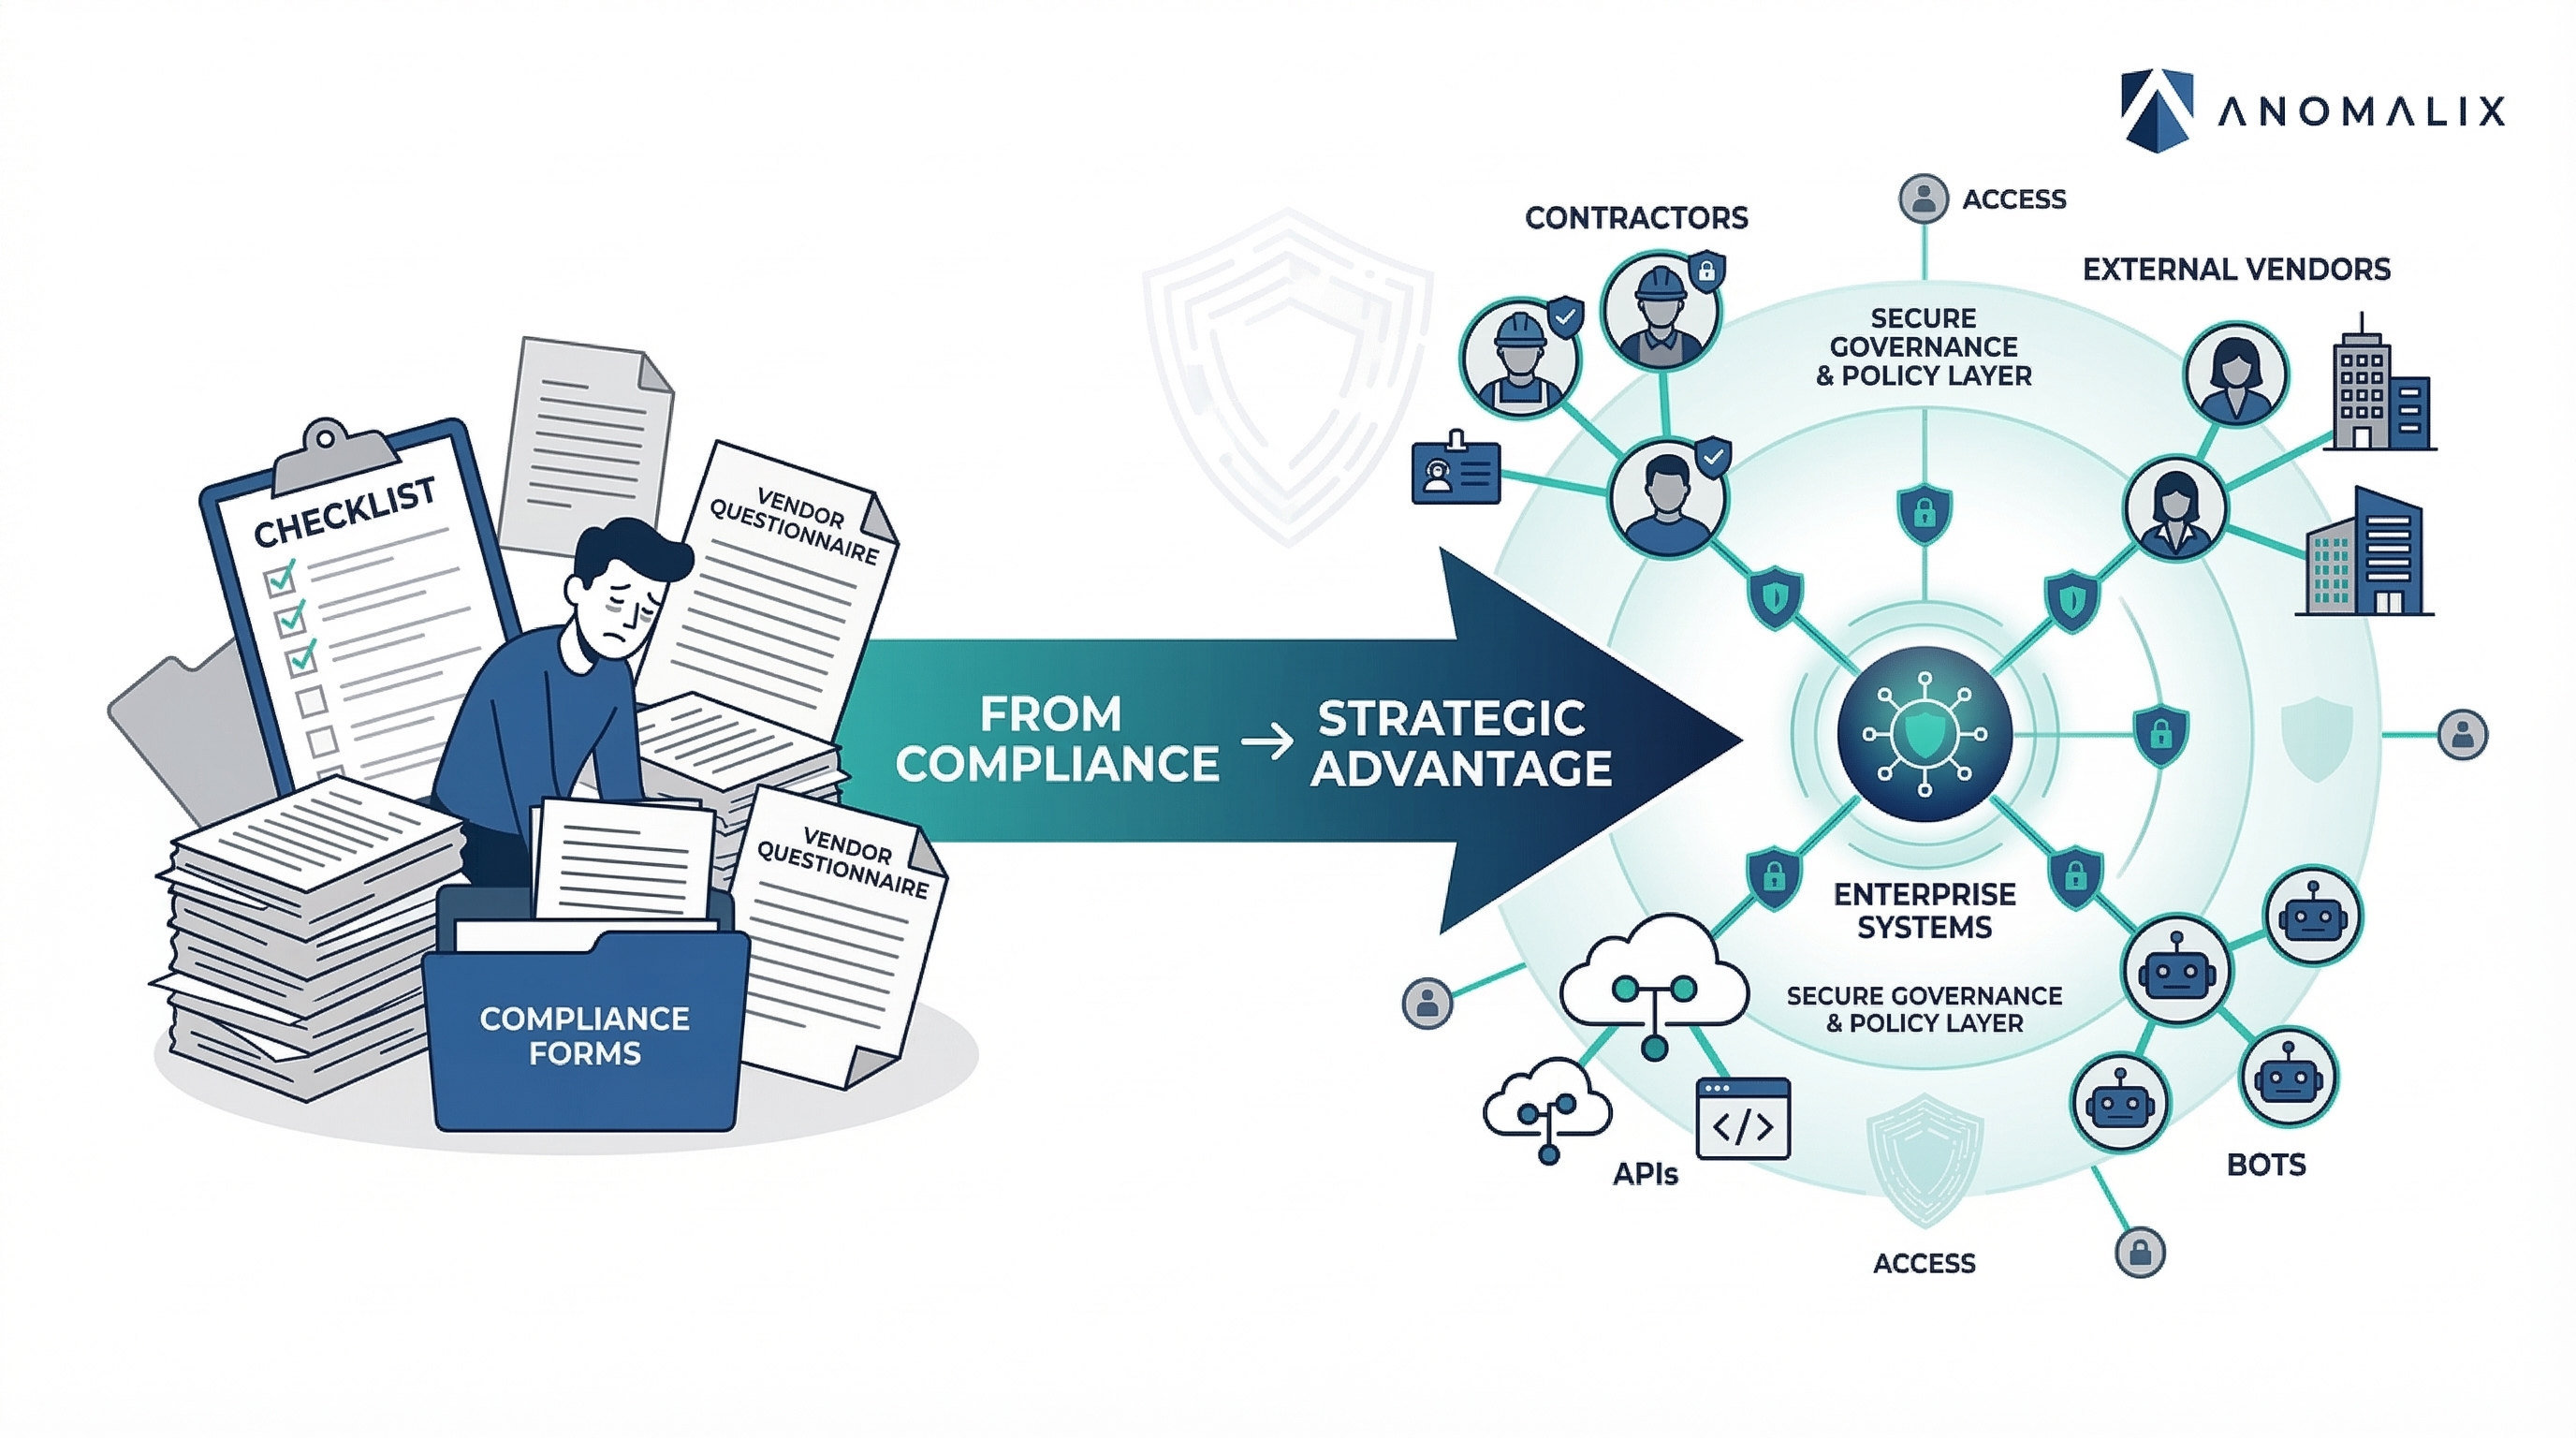
One of the biggest structural challenges in modern cybersecurity is that third-party identities do not clearly belong to any existing control system.
Different departments manage different aspects of vendor relationships:
Function
Focus
Procurement
Contracts and vendor selection
Vendor Management
Relationship governance
IAM
Employee identity management
Security Operations
Monitoring and threat detection
IT
Account provisioning
None of these systems fully govern the lifecycle of third-party identities.
Traditional identity and access management tools rely heavily on HR systems as the source of truth, which works well for employees but fails for external identities that originate from contracts, projects, or vendor relationships.
This creates a governance gap where:
- Vendor contracts exist without linked identity controls
- Identity accounts exist without lifecycle ownership
- Security tools see activity but lack business context
Closing this gap requires a fundamentally different approach to third-party risk management.
Identity-First Third-Party Risk Management
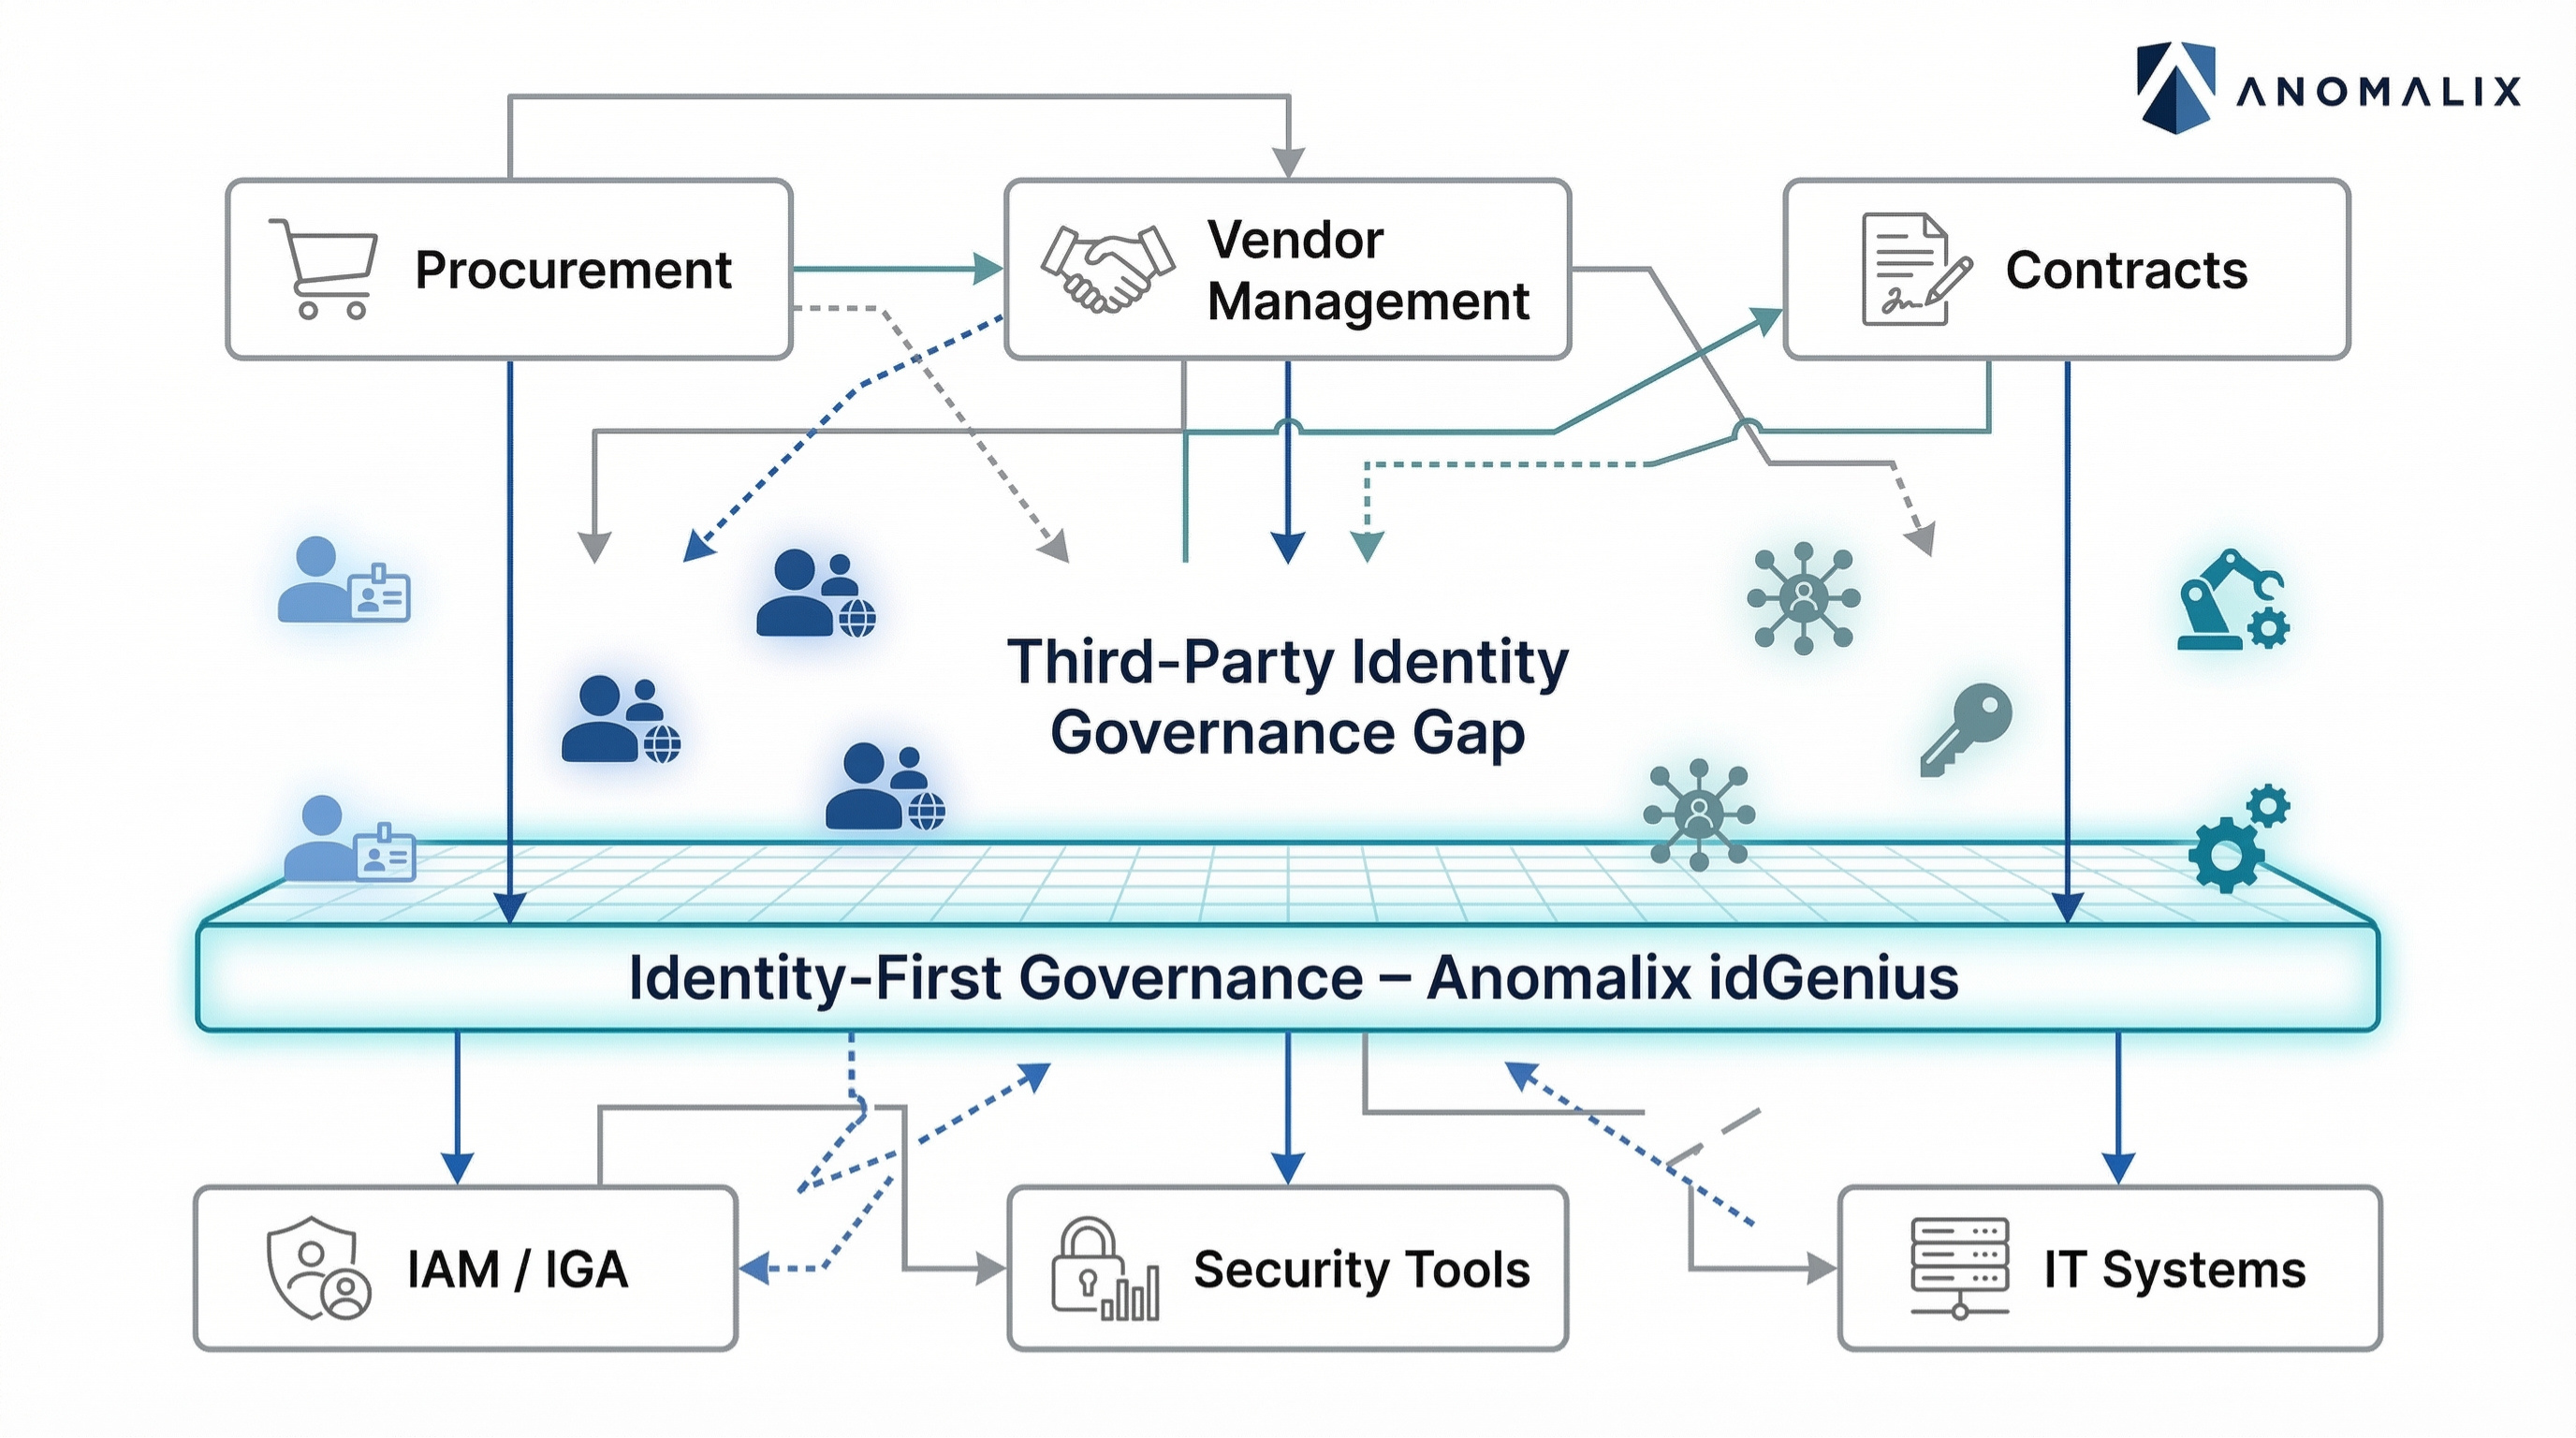
At Anomalix, we believe the future of TPRM is identity-first.
Identity-first third-party risk management shifts the focus from evaluating vendor organizations to governing the identities that interact with your environment.
Instead of asking:
“Is this vendor trustworthy?”
Identity-first TPRM asks:
- Which identities from this vendor have access?
- What systems and data can they reach?
- Why do they need that access?
- Who is accountable for it?
- When should it expire?
This shift transforms TPRM from a periodic assessment process into a continuous operational security capability.
Identity-first vendor governance ensures that every external identity is:
- Known
- Accountable
- Contextualized
- Time-bound
- Continuously monitored
This approach connects risk management directly to access governance, closing the gap between policy and operational security.
From Compliance Exercise to Strategic Capability
Organizations that rethink TPRM through an identity-first lens begin to see a significant transformation. Third-party risk management evolves from a reactive compliance task into a strategic business enabler.
1. Real-Time Visibility into the Extended Workforce
Identity-centric governance creates a centralized inventory of all external identities and their access.
Security teams gain visibility into:
- Third-party organizations
- Individual users and machine identities
- Access privileges and entitlements
- Project assignments and contract timelines
- Sponsoring business units
This level of transparency allows organizations to understand their true attack surface.
Without this visibility, security teams cannot answer even basic questions about external access.
2. Access Aligned with Business Context
Traditional access provisioning often happens without understanding the broader business relationship behind the request.
Identity-first TPRM ties access decisions directly to:
- Vendor contracts
- Project assignments
- Sponsoring departments
- Risk ratings
This ensures that external identities receive only the access required to perform their tasks, reinforcing least privilege principles.
Over time, this dramatically reduces the number of excessive permissions and dormant accounts in the environment.
3. Lifecycle Governance Instead of One-Time Reviews
External identities often move between roles, projects, and organizations. Their access needs change frequently.
An identity-first approach governs the entire lifecycle of these identities:
- Structured onboarding
- Policy-driven access provisioning
- Automated access adjustments
- Time-bound entitlements
- Automated offboarding
When access is tied directly to engagement timelines, dormant accounts disappear by design rather than by manual cleanup.
4. Continuous Risk Intelligence
In traditional TPRM programs, risk assessments occur periodically.
Identity-first governance enables continuous risk monitoring by linking identity activity to security analytics.
Risk signals may include:
- Unusual access behavior
- Dormant accounts
- Privileged entitlements
- Access from unexpected geographies
- Vendor breach notifications
This dynamic risk model allows organizations to adjust controls in real time rather than waiting for the next assessment cycle.
Business Benefits of Strategic Third-Party Risk Management
When third-party risk management evolves beyond compliance, organizations experience tangible business advantages.
Faster Vendor Onboarding
Manual vendor onboarding processes often delay projects.
Automated identity workflows enable organizations to onboard external users quickly while maintaining security controls.
This improves collaboration without increasing risk.
Reduced Security Incidents
Identity governance significantly reduces common breach vectors such as:
- Orphaned vendor accounts
- Over-privileged contractor access
- Shared or unmanaged service accounts
By governing these identities continuously, organizations shrink their attack surface.
Stronger Compliance and Audit Readiness
Regulators increasingly expect organizations to demonstrate control over third-party access.
Frameworks such as:
- PCI DSS
- ISO 27001
- SOC 2
- GDPR
- NIST CSF
all emphasize strong identity governance and least-privilege enforcement.
Identity-first TPRM provides audit-ready visibility into:
- Who has access
- Why they have it
- Who approved it
- When it will expire
This dramatically simplifies audit preparation and reduces compliance risk.
Stronger Vendor Trust and Collaboration
When organizations implement structured identity governance, vendor relationships become more transparent and predictable.
Vendors benefit from:
- Faster access provisioning
- Clear onboarding requirements
- Defined responsibilities
- Consistent processes
This improves operational efficiency across the digital supply chain.
The Anomalix Point of View
At Anomalix, we believe the future of cybersecurity is identity-driven—and third-party identities are the most overlooked part of that equation.
Modern enterprises rely on external ecosystems to operate, yet most identity security strategies remain focused almost entirely on employees.
This mismatch creates systemic blind spots where risk accumulates.
Our perspective is clear:
Identity is the control plane of modern cybersecurity, and third-party identities must be governed with the same rigor as internal users.
Through the idGenius platform, Anomalix helps organizations operationalize identity-first third-party risk management by providing:
- Centralized visibility into third-party organizations and identities
- Contract- and project-based access governance
- Automated lifecycle management
- Time-bound access enforcement
- AI-driven risk intelligence and anomaly detection
By aligning identity governance with vendor lifecycle management, idGenius enables organizations to move beyond reactive compliance and toward proactive security.
Conclusion: Turning Third-Party Risk into Strategic Advantage
Third-party risk management is at a turning point.
The traditional model—focused on vendor questionnaires and periodic assessments—was built for a different era. In today’s digital ecosystem, risk flows through identities and access paths, not just through vendor relationships.
Organizations that continue to treat TPRM as a compliance function will struggle to keep pace with the complexity of the extended enterprise.
But organizations that rethink TPRM as an identity governance discipline unlock something far more powerful: a strategic advantage.
With identity-first third-party risk management, organizations gain:
- Visibility into their extended workforce
- Real-time control over external access
- Continuous risk intelligence
- Faster collaboration with partners and vendors
- Stronger security and compliance outcomes
Most importantly, they move from reacting to third-party risk to actively governing it.
The future of third-party risk management isn’t just about assessing vendors—it’s about governing the identities that connect your business to the world.
Contact us at info@anomalix.com to learn how our idGenius platform can help you govern your extended workforce with confidence, security, and ease.